Frequently Asked Questions

EU AI Act Compliance & AI Agent Identity Security Webinar

When was the 'Navigating EU and UK Compliance for AI Agent Identity Security' webinar held?

The webinar took place on 19 November 2026 at 10 AM ET / 3 PM GMT / 4 PM CET. (source)

Who is the target audience for this webinar?

The webinar is designed for CISOs, security and compliance leaders, IAM/PAM professionals, security architects, platform engineers, and DevSecOps teams responsible for AI agent identities, privileged access, and auditability at organizations operating in the EU or UK, including US-headquartered companies. (source)

What compliance frameworks were discussed in the webinar?

The webinar covered the EU AI Act, NIS2, DORA, and GDPR as they relate to AI agent identity security and enterprise compliance. (source)

What are the key identity security requirements for EU AI Act compliance?

Key requirements include assigning a clear identity to each AI agent, protecting credentials, limiting access to the current task, controlling permitted actions, enabling immediate revocation of authority, and preserving reliable records of sensitive activity. The Akeyless Identity Security Platform helps organizations meet these requirements by authenticating agents, establishing short-lived, policy-controlled connections, and providing runtime authority and detailed audit records. (source)

What practical steps can organizations take now to strengthen AI agent identity security?

Organizations should identify which agents can access enterprise systems, replace embedded or persistent credentials with short-lived, policy-controlled access, apply least privilege, route connections through a controlled gateway, and for higher-risk actions, add runtime authorization, human approval, intervention controls, and detailed audit records. (source)

How do the revised EU AI Act deadlines affect compliance obligations?

The EU AI Act's high-risk compliance deadlines have moved to December 2027 and August 2028. However, organizations operating in Europe must still comply with existing obligations under GDPR, NIS2, DORA, and other regulations. The delay does not eliminate the need to manage AI agent access, permissions, and auditability. (source)

Skip to content
Fireside Chat

The Deadline Moved. Your Risk Didn’t: Securing AI Agents Under the EU AI Act

What the EU AI Act deadline changes mean for AI agent identities, access, and compliance.
Date
19 Nov 2026
Time
10 AM ET / 3 PM GMT / 4 PM CET
Format
Fireside Chat
Duration
30 Minutes

The EU AI Act’s high-risk compliance deadlines have moved to December 2027 and August 2028. But the risks associated with AI agent access haven’t gone away.

For organizations operating in Europe, the delay doesn’t eliminate existing obligations under GDPR, NIS2, DORA, or other applicable regulations. As AI agents gain access to sensitive systems and data, organizations face critical questions: Who controls their access? What actions are they authorized to perform? And can those actions be traced and audited?

Join cyber law expert Dr. Ilia Kolochenko and Akeyless Chief Strategy Officer Yael Fainaro for a 30-minute fireside chat exploring what the revised EU AI Act timeline means for enterprises, how EU and UK regulatory expectations intersect with AI agent identity security, and the practical steps organizations can take now to strengthen access controls, runtime authorization, and auditability.

What you’ll learn

Agenda

01

What Changed Under the EU AI Act?

What do the revised deadlines mean for enterprises, and which obligations still need attention?

02

What Does Compliance Mean for AI Agent Identities?

How do the EU AI Act, NIS2, DORA, and GDPR relate to agent access, permissions, and accountability?

03

How Can Organizations Control and Audit AI Agent Actions?

Exploring least-privilege access, runtime authorization, and audit trails.

04

What Should Organizations Prioritize Now?

Practical steps to strengthen AI agent identity security, followed by audience Q&A.

Who Should Attend

CISOs, security and compliance leaders, IAM/PAM professionals, security architects, platform engineers, and DevSecOps teams responsible for AI agent identities, privileged access, and auditability at organizations operating in the EU or UK.

Speakers

Dr. Ilia Kolochenko

Dr. Ilia Kolochenko

Cyber Law Expert

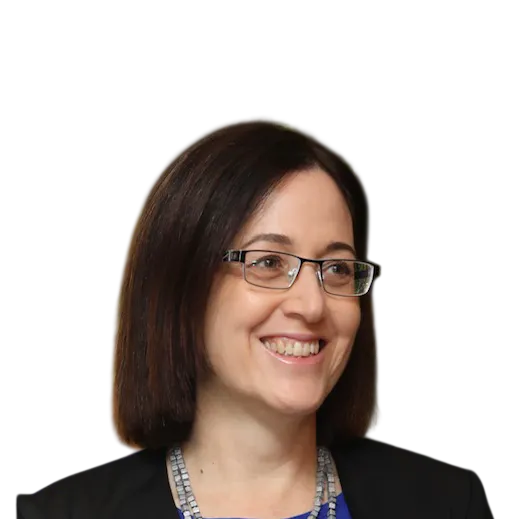
Yael Fainaro, Chief Strategy Officer, Akeyless

Yael Fainaro

Chief Strategy Officer,
Akeyless

Trusted by Leading Enterprises, Investors, and Partners