

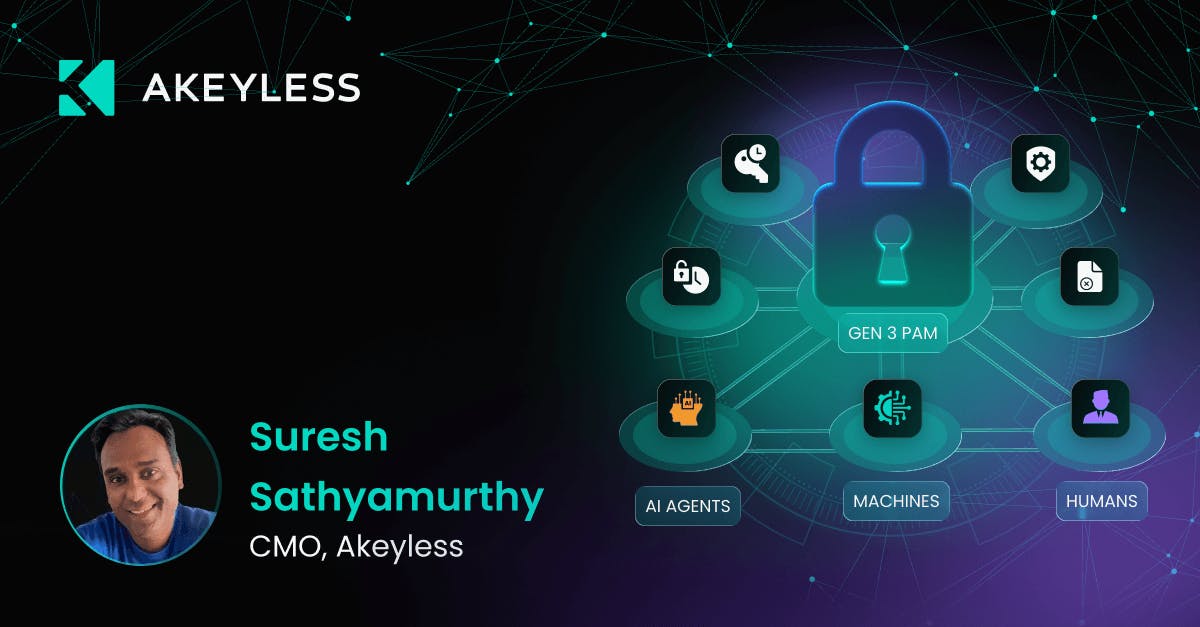
Privileged access is evolving. Learn how Gen 3 PAM eliminates standing privileges and secures humans, machines, and AI with unified identity security.
Secure connectivity between every agent and system, control actions with intent-aware access, and audit all activity
Trusted by Leading Enterprises, Investors, and Partners






Reduce risk and simplify access by replacing standing privileges and shared credentials across every environment.
People still need access, but they have more of it than they should, for longer than they should. Standing privileges and shared credentials leave critical systems exposed.
Secure identities through precise, time-limited access, strong authentication, and consistent governance—deployed in days.

Akeyless uses federated identity and policy-based workflows to control access to systems and applications. Permissions are granted only when needed and automatically expire, replacing static roles and standing privileges.
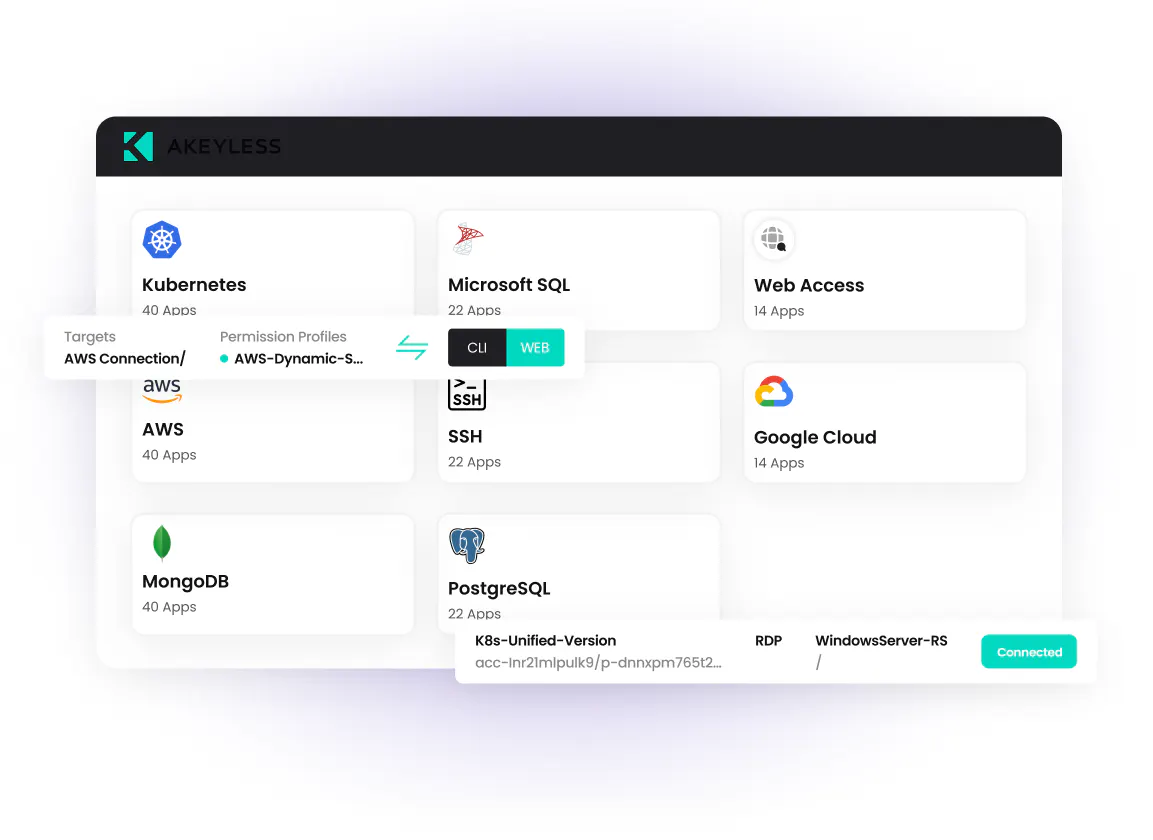
Users access servers, databases, cloud consoles, and internal applications through brokered, time-bound sessions. No direct logins, shared credentials, or VPNs are required.

Akeyless secures and automatically rotates shared and legacy credentials. Zero-knowledge Distributed Fragments Cryptography® ensures credentials are never exposed or handled by users.

Akeyless applies consistent, least-privilege policies across cloud, SaaS, and on-prem systems. Every session and action is recorded in a unified audit trail, supporting compliance requirements and accelerating investigations.
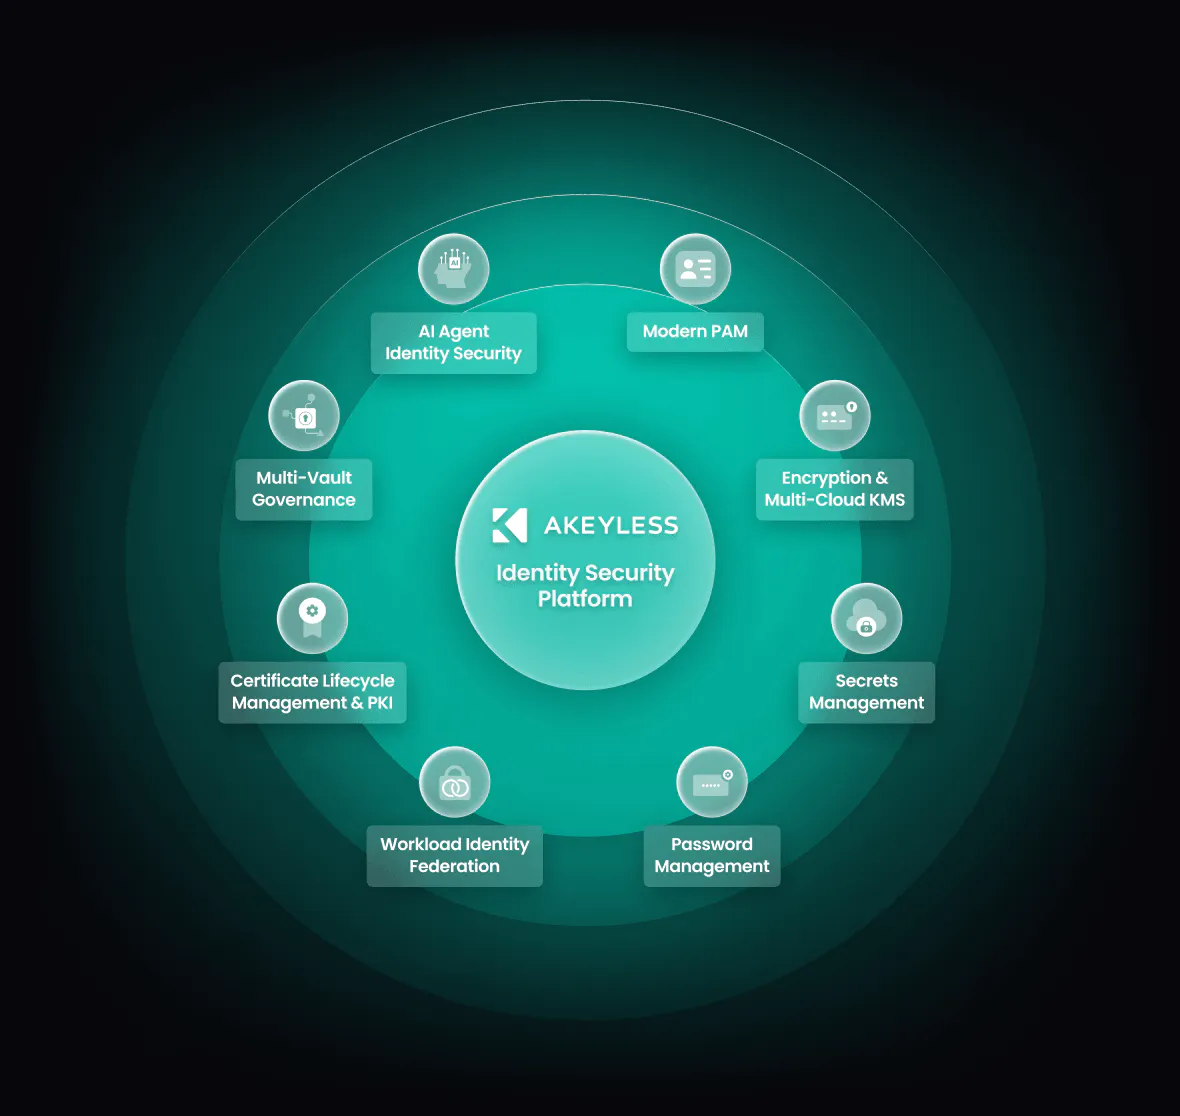
The Akeyless Identity Security Platform unifies AI agent, machine, and human access under one zero-knowledge, cloud-native foundation.
With Akeyless, organizations eliminate secrets, automate credential lifecycles, and enforce Zero Trust at every level, from code to console.



Privileged access is evolving. Learn how Gen 3 PAM eliminates standing privileges and secures humans, machines, and AI with unified identity security.
Insights, benchmarks, and real-world data on how AI agents are reshaping identity risk and what organizations must do next.
Identity Security Unleashed brings together practitioners and thought leaders to explore how identity security must evolve in the age of AI.
Legacy PAM is too slow, complex, and costly for today’s multi-cloud, automation-driven enterprises.
Answers to the Most Common Questions About Akeyless Identity Security for Humans