

Add unified RBAC, audit, and visibility across HashiCorp Vault and cloud secrets managers without migrating secrets or disrupting existing workflows.
Centralize visibility, policy, and compliance across every vault without moving a single secret.
Trusted by Leading Enterprises, Investors, and Partners







Calculate the full cost of HashiCorp Vault, including infrastructure, operations, upgrades, and engineering time. Then see how much you can save on secrets management with Akeyless.
Connect Akeyless to your existing secrets managers to centrally govern, secure, and automate secrets across your environment, without replacing your existing infrastructure.


Centralize governance, visibility, and operations while allowing teams to keep the vaults that work best for them.
Most organizations don't have one vault. Cloud providers, Kubernetes platforms, enterprise vaults, and AI systems each introduce their own secret stores. Multiple vaults give teams flexibility, but unmanaged fragmentation creates real consequences. Secrets become harder to track, policies become inconsistent, and governance becomes more difficult, increasing both operational burden and security risk.
Most organizations rely on multiple vaults across clouds, platforms, and teams. Akeyless brings them together under a unified operational and governance model.

Connect HashiCorp Vault, AWS Secrets Manager, Azure Key Vault, Google Secret Manager, Kubernetes Secrets, and other secret stores without migration. Akeyless acts as a centralized control plane while secrets remain in their existing vaults.
Manage secrets across clouds, platforms, and teams from a single interface. Gain centralized visibility into secret locations, ownership, and access without switching between tools.
Create, update, delete, and rotate secrets across supported vaults from the Akeyless console, CLI, or SDKs. Streamline operations through a consistent management experience regardless of where secrets are stored.
Use Akeyless authentication methods, access controls, and governance policies across connected vaults. Enforce consistent security standards while preserving flexibility across teams and environments.
Explore key features of Akeyless Multi-Vault Governance
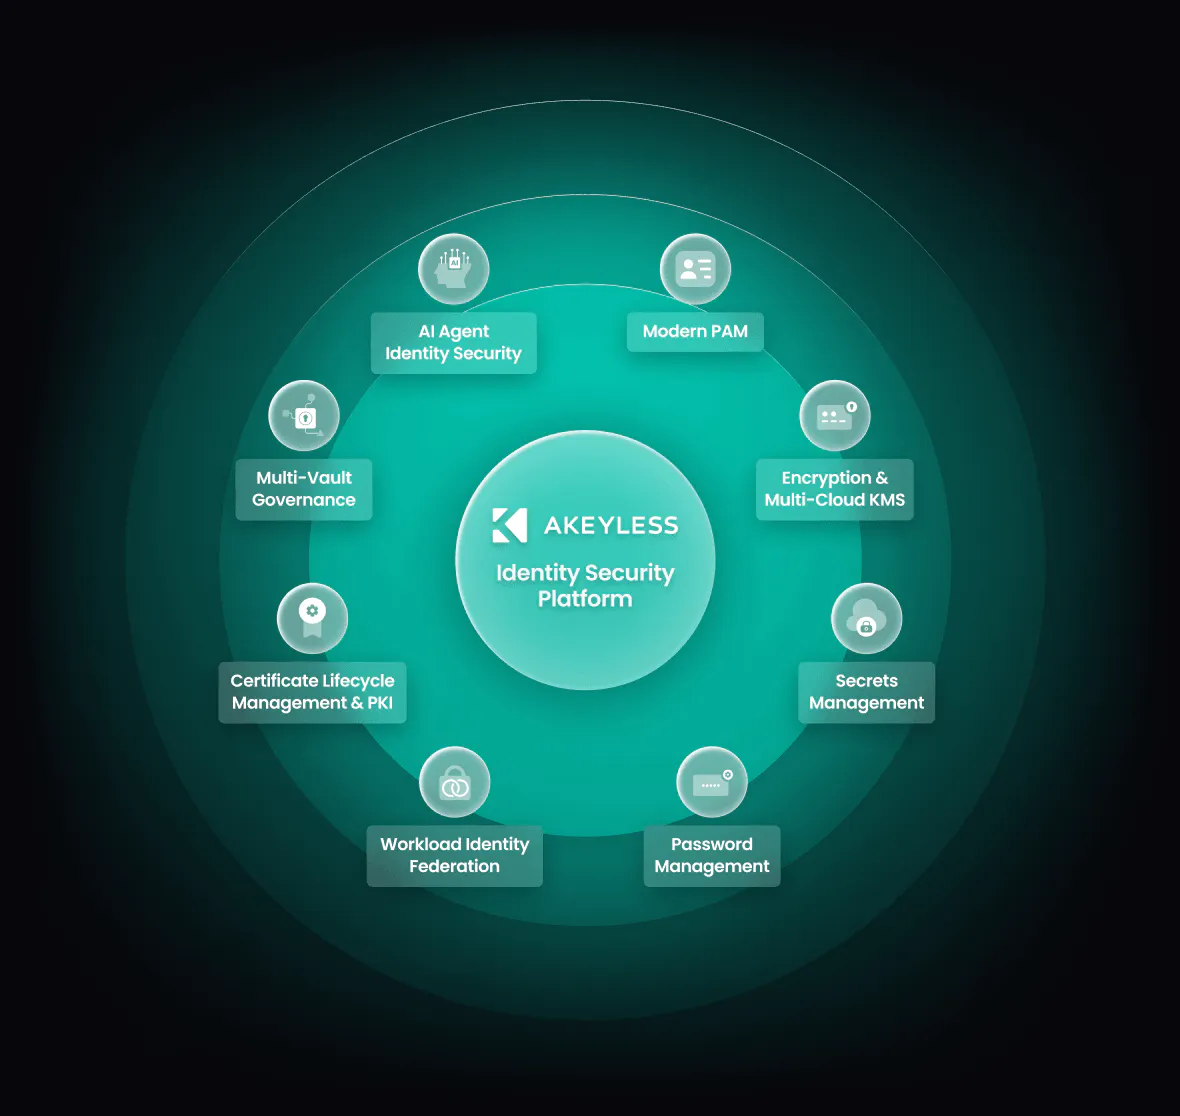
Secrets, machine identities, certificates, privileged access, and AI agents all require consistent control across modern environments. Managing them separately creates gaps in security, policy, and visibility.
Akeyless unifies Privileged Access, Secrets Management, KMS, Certificate Lifecycle Management, and AI agent security into a single SaaS platform with one policy engine and centralized governance across every identity.



Add unified RBAC, audit, and visibility across HashiCorp Vault and cloud secrets managers without migrating secrets or disrupting existing workflows.
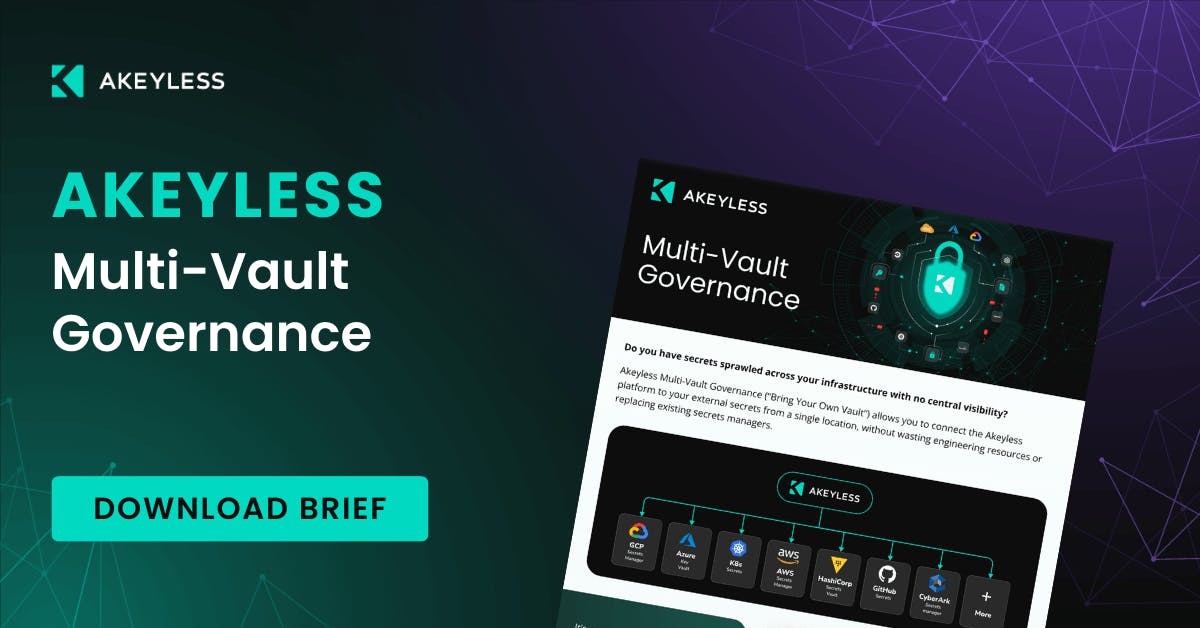
Akeyless Multi-Vault Governance (“Bring Your Own Vault”) allows you to connect the Akeyless platform to your external secrets from a single location, without wasting engineering resources or replacing existing secrets managers.

Vault sprawl and fragmented secrets management are driving risk, cost, and audit complexity across multi-cloud environments. This session shows how Akeyless Multi-Vault Governance centralizes visibility, policy, and rotation across existing vaults, without migration, delivering unified control, reduced overhead, and Zero-Knowledge security at scale.
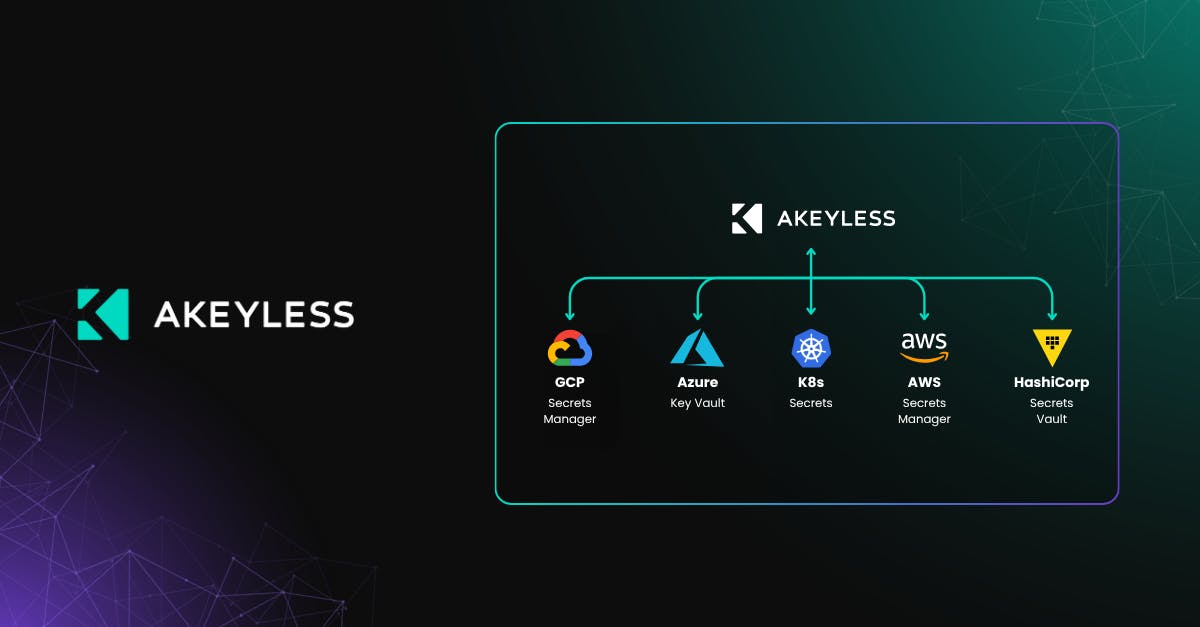
Akeyless simplifies secrets migration by giving organizations two secure options: unify existing secret stores under one centralized management layer or automate migration into Akeyless when consolidation is needed. The platform connects to systems such as AWS Secrets Manager, Azure Key Vault, Google Secret Manager, HashiCorp Vault, and Kubernetes to enable full multi-vault governance without downtime or scripting.