

Live demo of controlling AI agent access, actions, and secrets at runtime
Protect the credentials AI agents use, control what agents do with intent-aware enforcement, and audit every action with full attribution
Trusted by Leading Enterprises, Investors, and Partners






Guide
Learn practical ways to secure agent identities, control access, and govern actions at runtime.
Live Demo
See how Akeyless Agentic Runtime Authority enables secure AI agent access with just-in-time credentials, runtime policy enforcement, and full auditability.
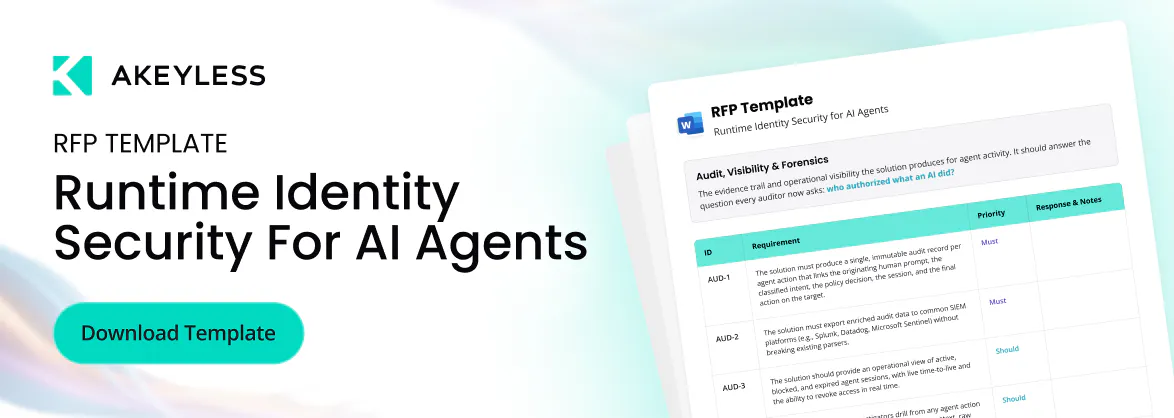
RFP Template
Download this ready-to-use RFP template to simplify vendor selection with a structured framework for evaluating runtime security solutions that protect autonomous AI agents.
Remove standing access, ensure actions align with approved intent, and maintain accountability for everything agents do.
AI agents operate with too much power and too little oversight. Your coding agent may hold standing keys to production, or find ones you never gave it, sitting in a config file or memory store. Your customer service agent might pull records a human in the role can't and shouldn't. Traditional access control cannot determine intent or keep up with agents acting autonomously in milliseconds. By the time they detect misuse, the damage is done.
of organizations hardcode AI agent credentials directly in workflows*
YoY growth in leaked AI-service credentials on GitHub**
secrets exposed in MCP config files in 2025**
an AI coding agent found an over-privileged credential and deleted a production database***
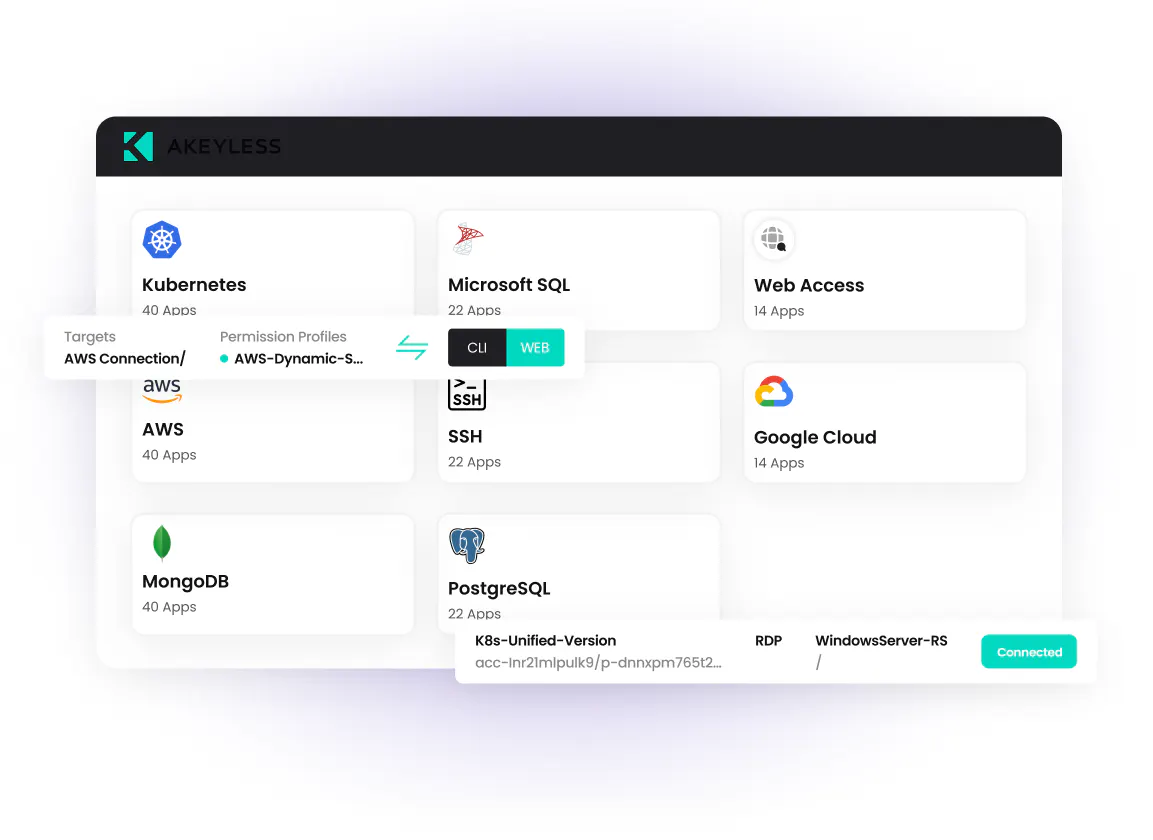
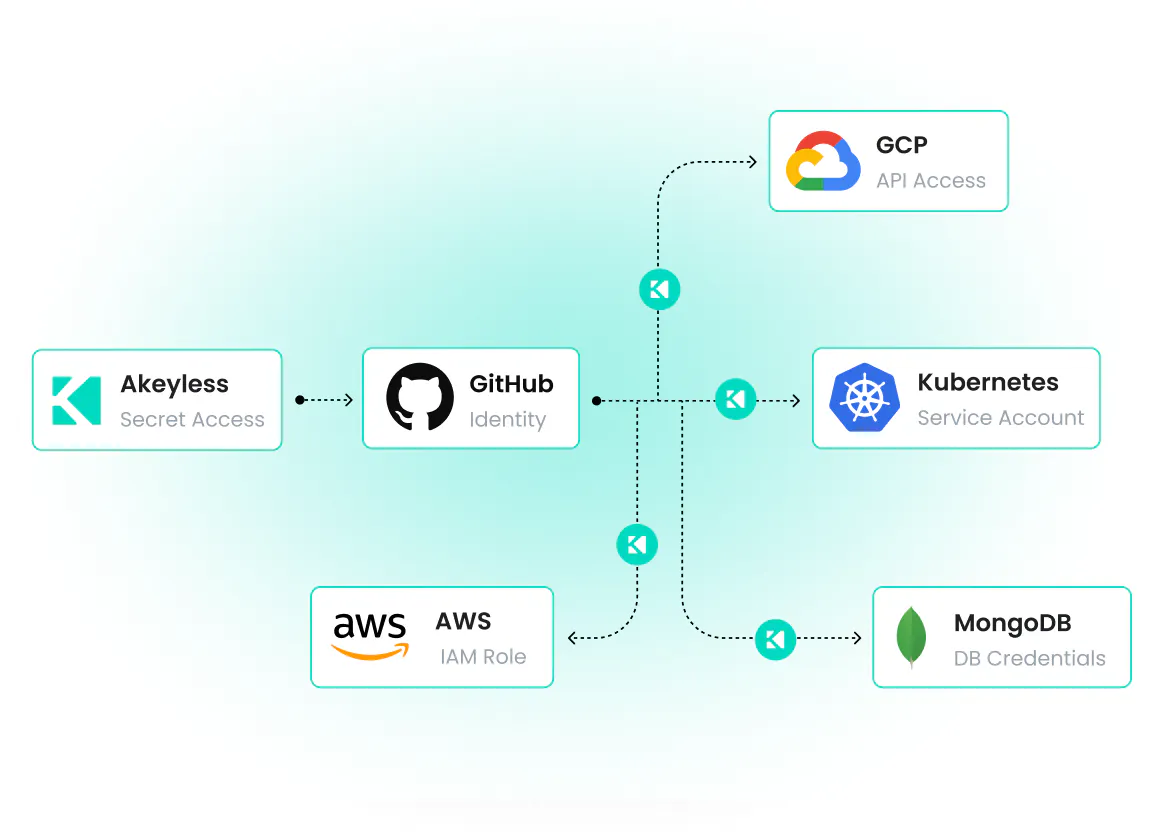
Remove standing credentials entirely with Akeyless SecretlessAI®. Akeyless brokers access through the Gateway and generates scoped, short-lived access for each task across SaaS, web apps, and infrastructure alike. AI agents never receive a secret—no storage, no privilege buildup, and nothing for a compromised or prompt-injected agent to steal.
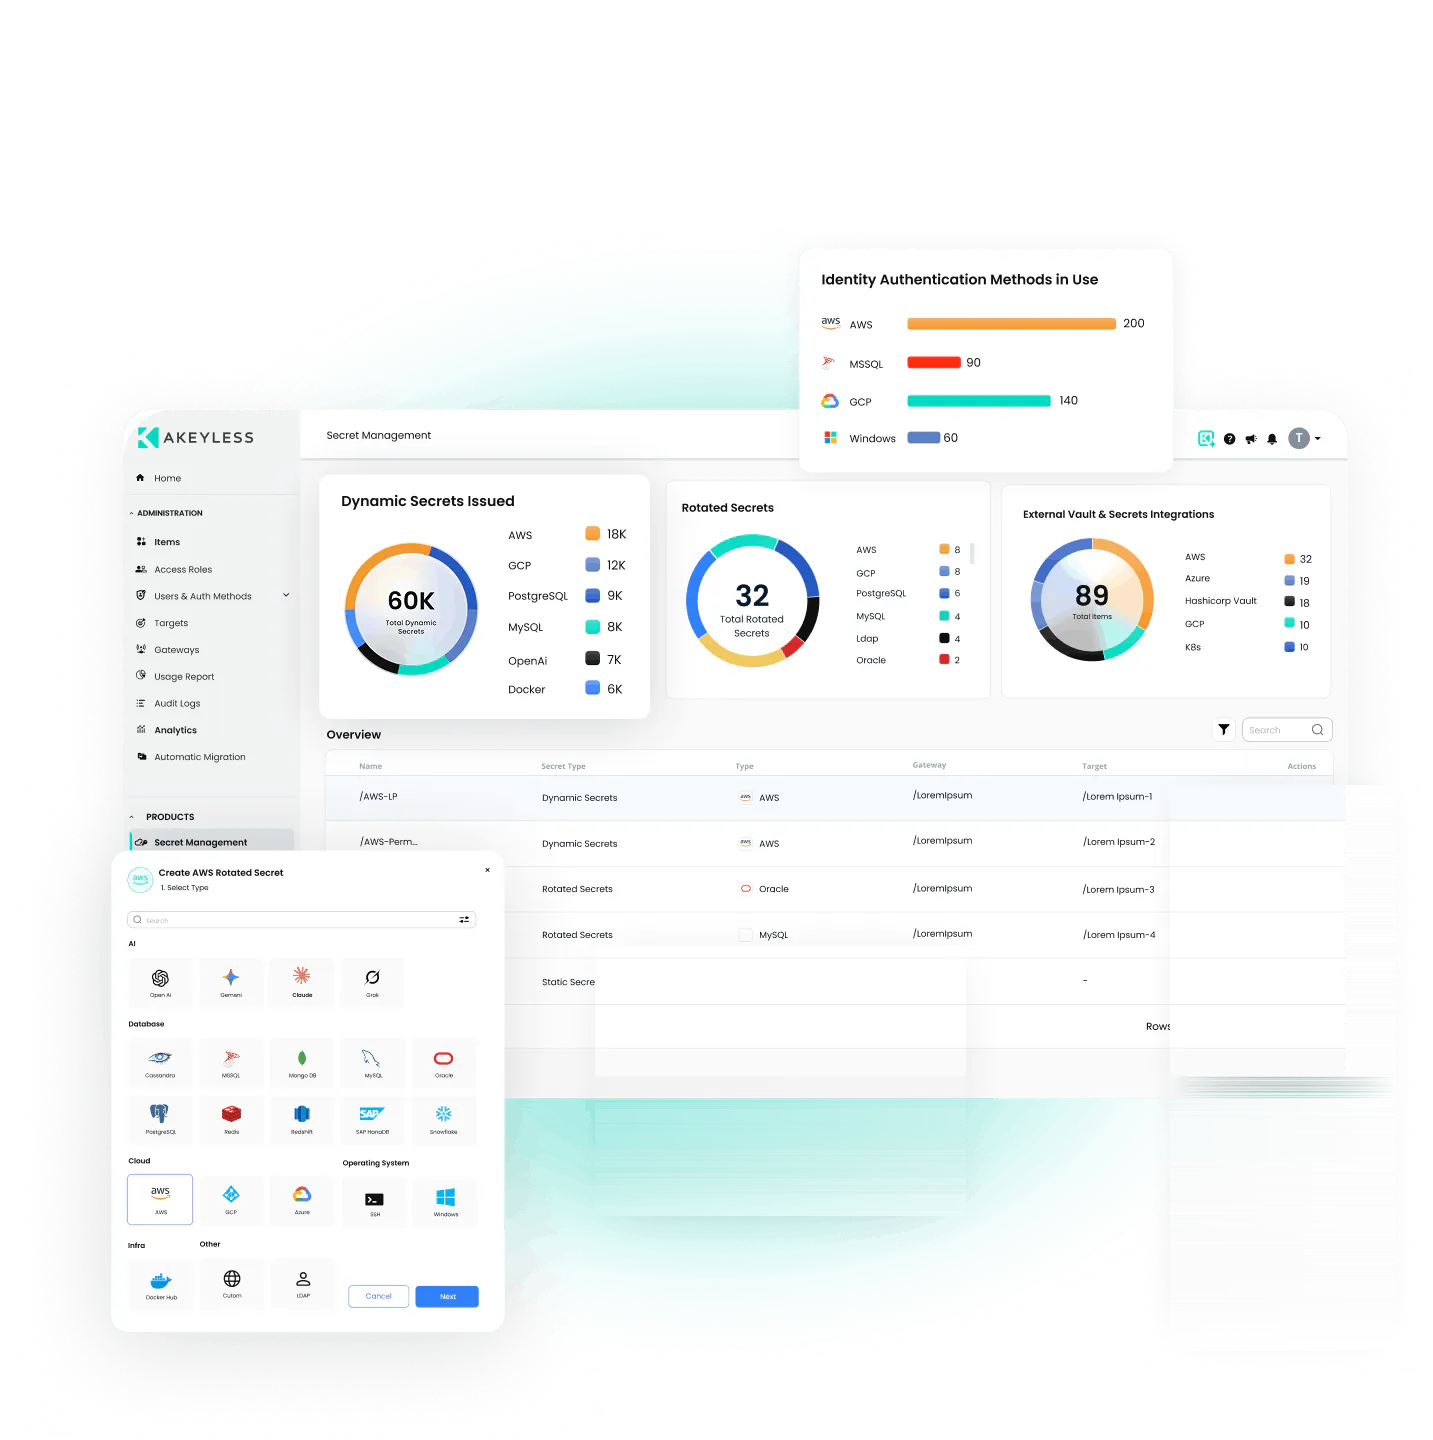
Not every agent can go fully secretless from the outset. Some still need direct credentials: passwords, API keys, certificates, cryptographic keys. Akeyless governs their issuance, rotation, and revocation under centralized policy, so nothing goes unmanaged or forgotten.
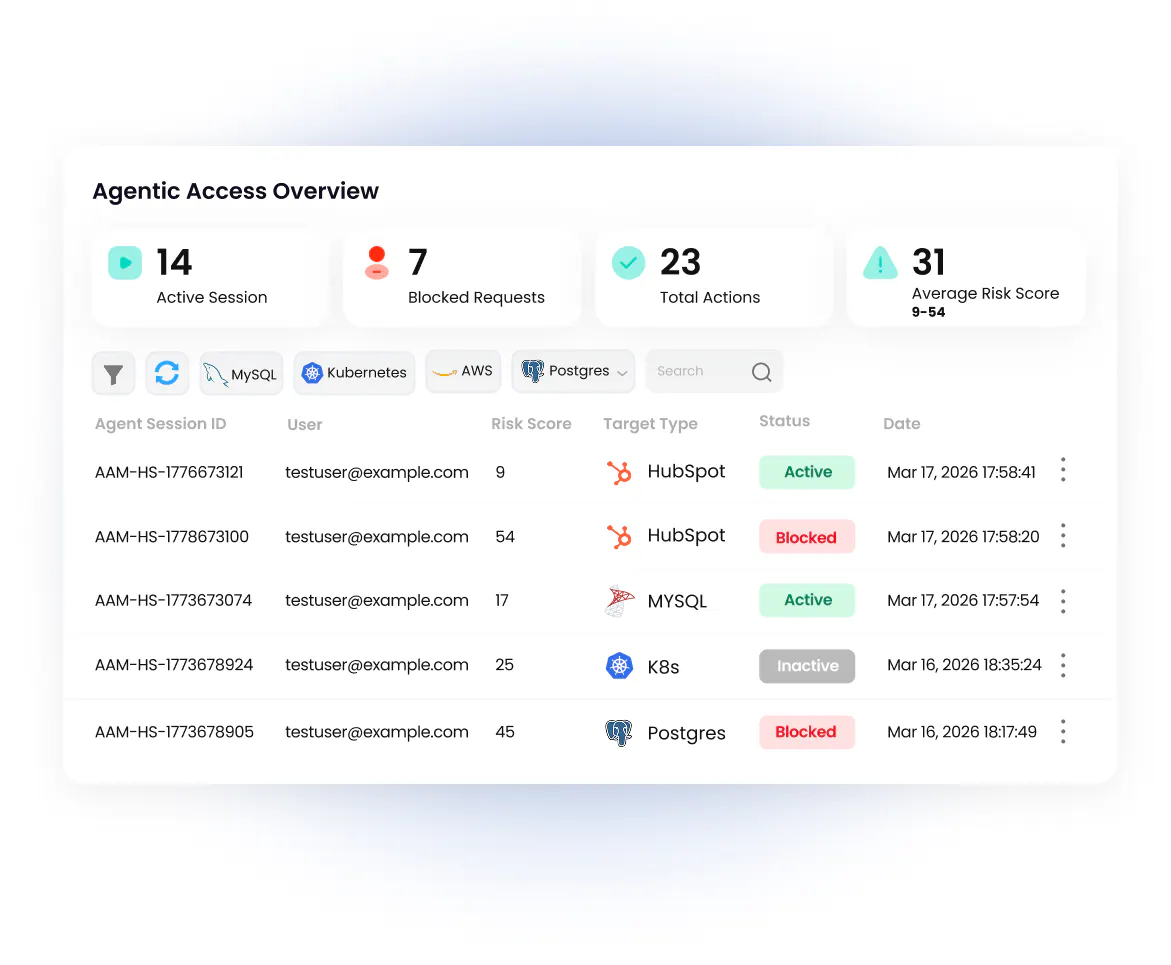
Assess the semantic intent behind each request and constrain the agent to the authority appropriate for the task—even when the underlying user or identity has broader permissions. Enforce policy at runtime to block unauthorized actions and filter or mask sensitive output. Any session can be shut down instantly with a real-time kill switch.
Discover orphaned credentials, stale tokens, and overbroad access that agents could exploit. Identify and prioritize the ones with real potential for harm, and route them to remediation.
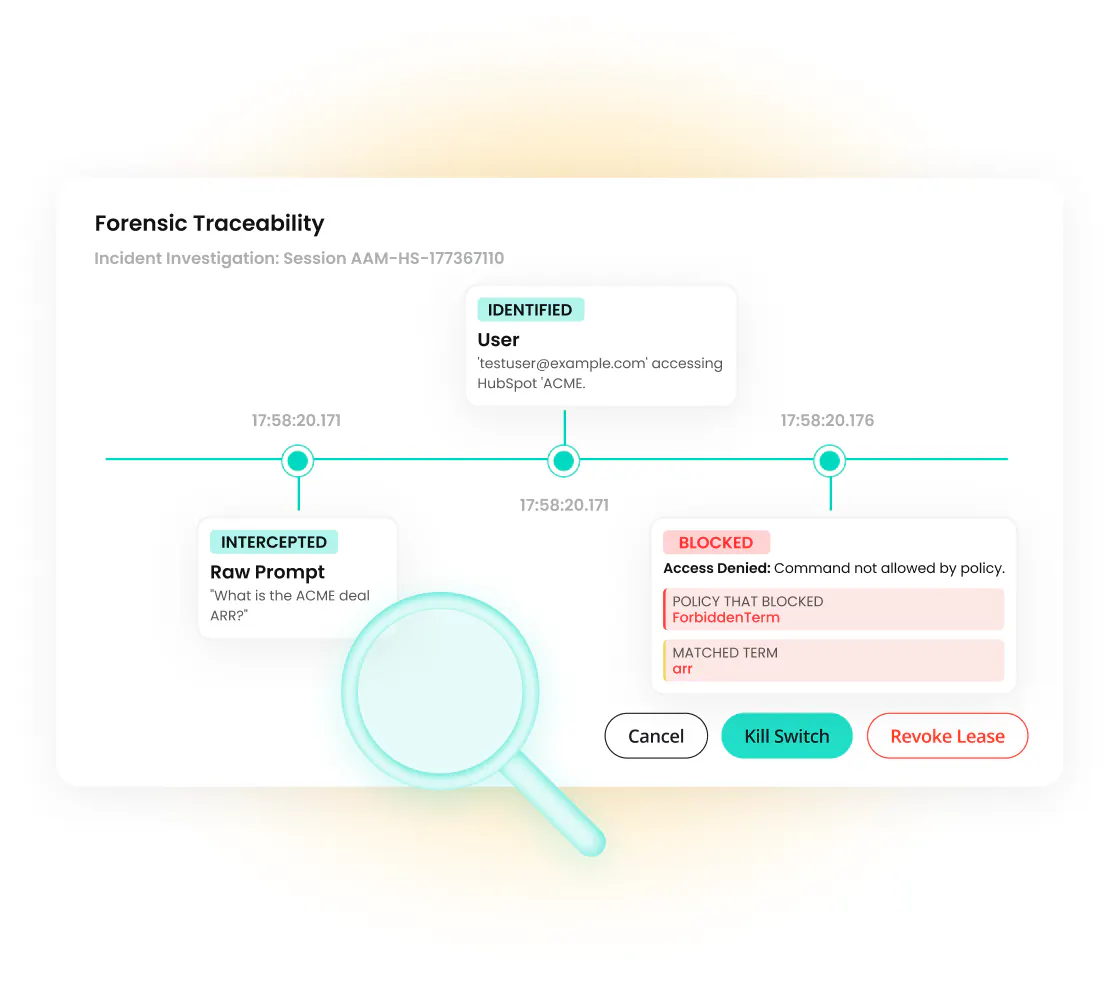
Eliminate the AI black box. Log every credential use and every action, and trace each one back to the human, machine, or agent behind it. One complete forensice audit trail, spanning both credential access and activity.
Credential protection, activity protection, and governance and visibility, in one platform.
Every agent request is intercepted before reaching its target, evaluated against declared intent, and continuously inspected during execution. Live commands across SSH, databases, Kubernetes, and cloud APIs are monitored and blocked immediately if they exceed approved authority.
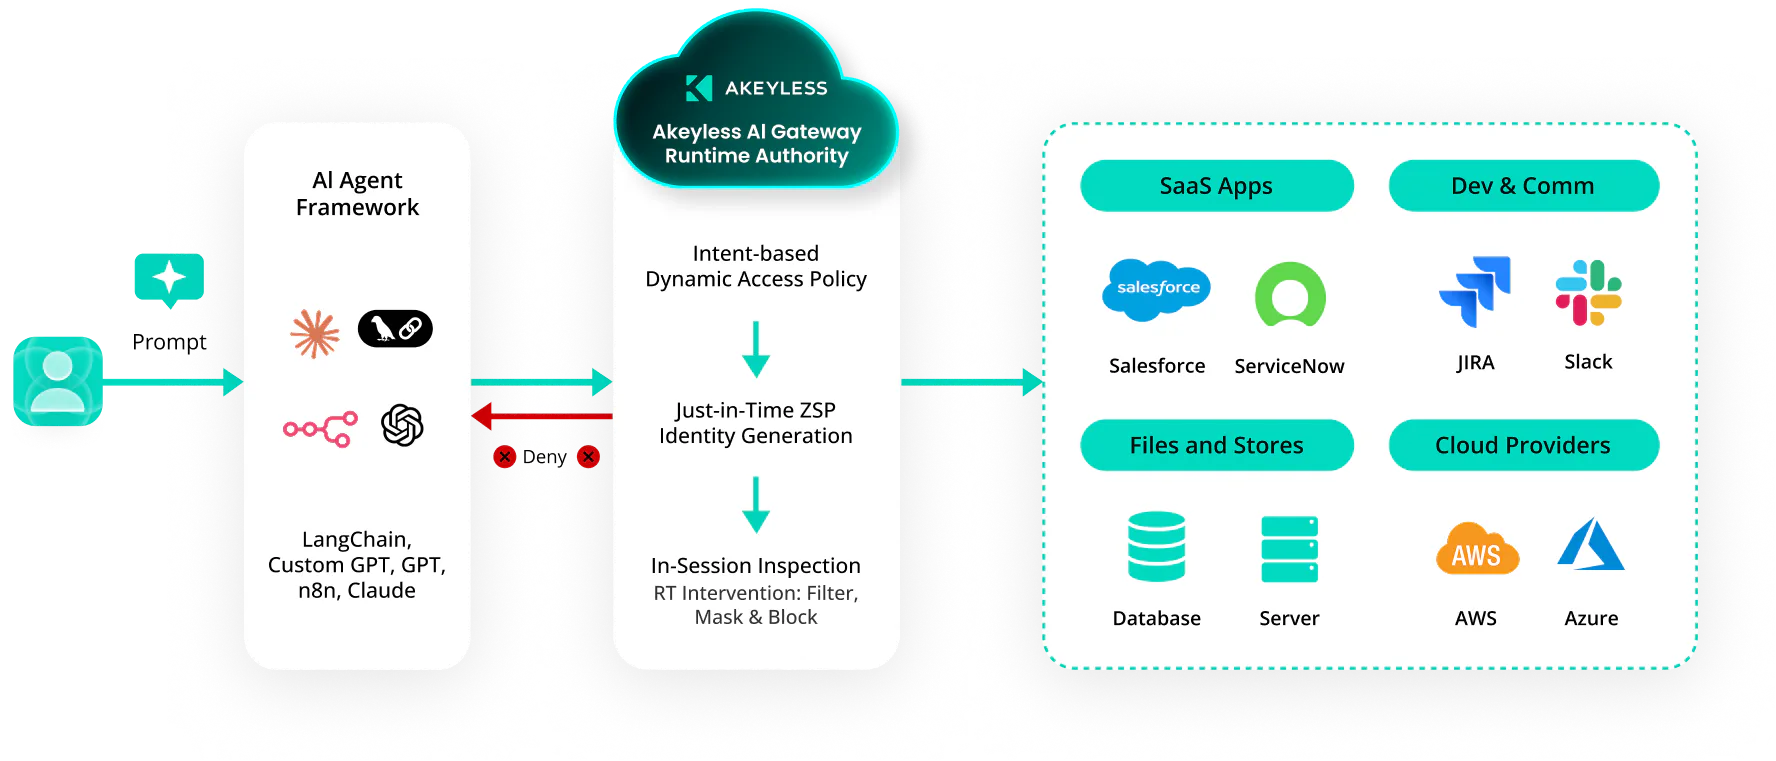
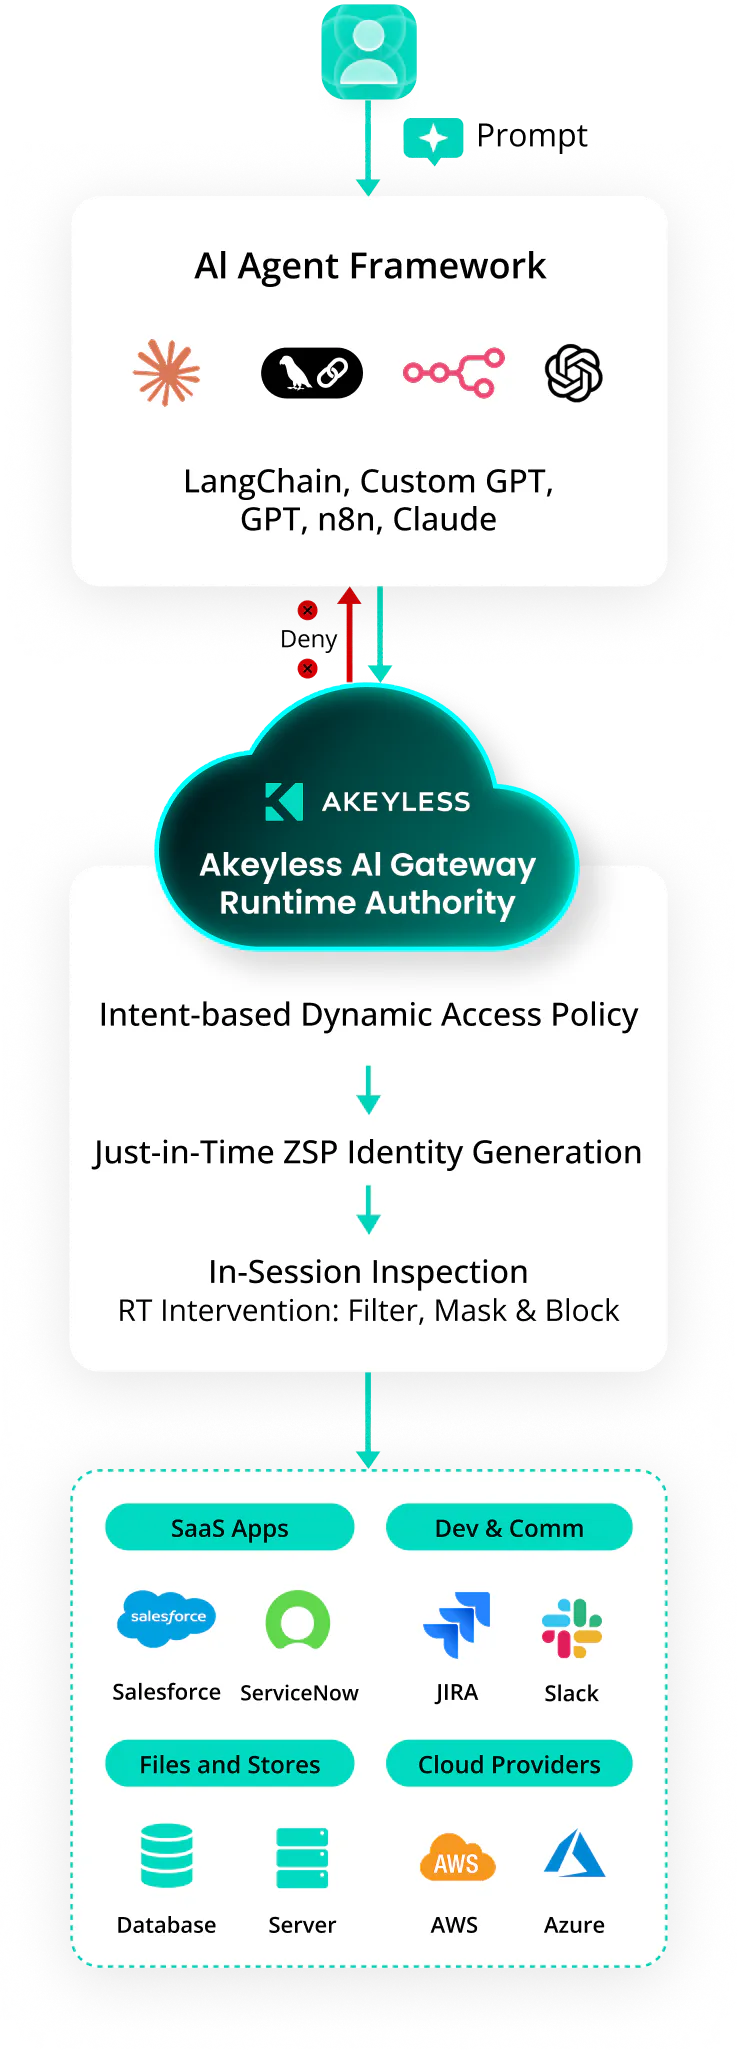
With Agentic Runtime Authority, you don't just hope your AI behaves. You enforce its boundaries at the Gateway level, and you maintain a tamper-proof forensic audit trail of every single prompt and API call it attempts to make.
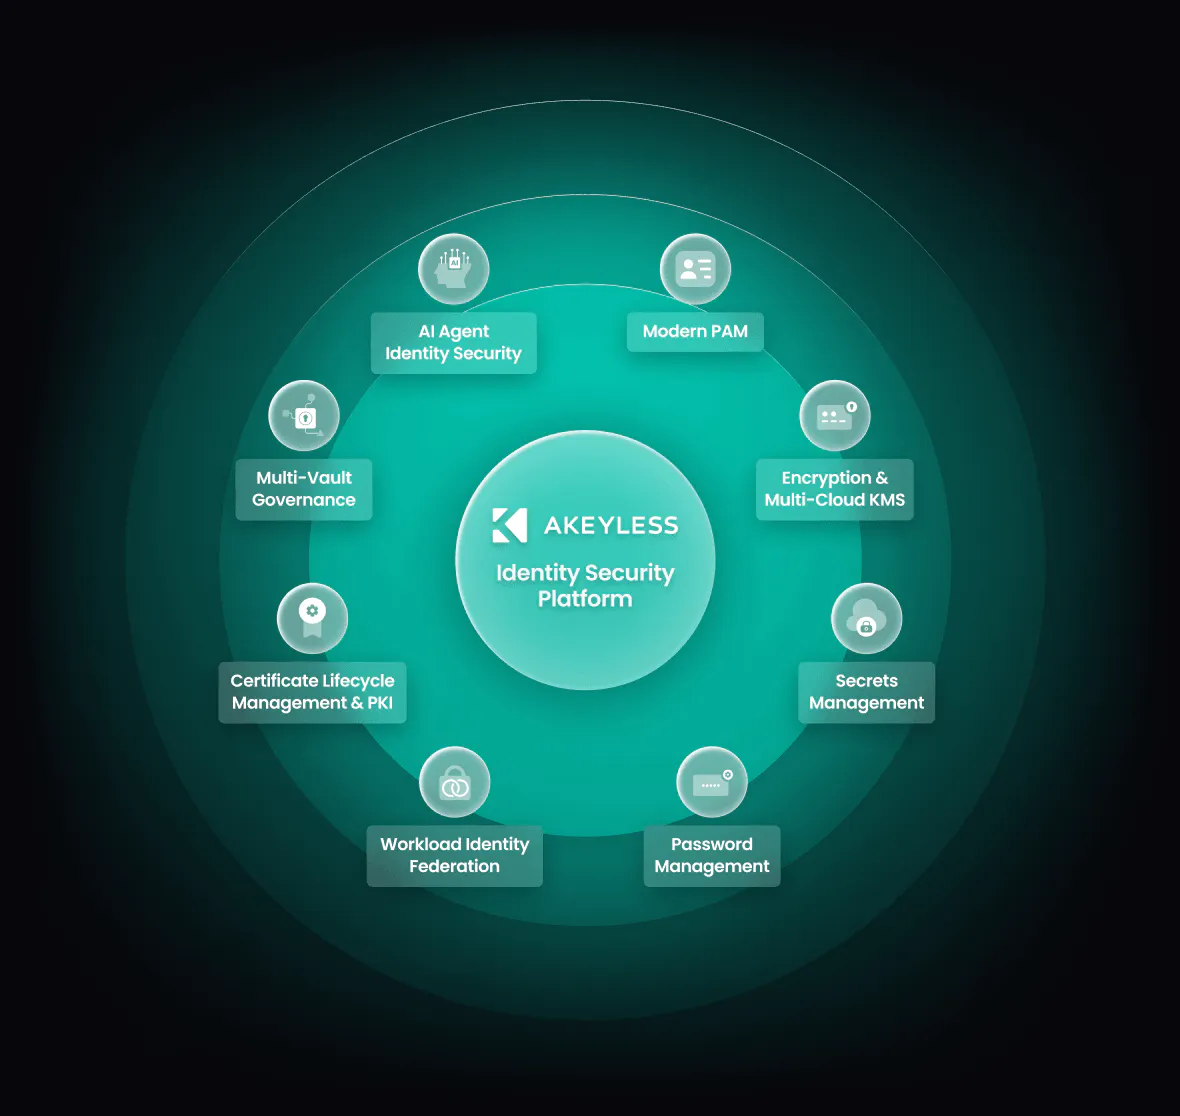
AI agent security does not exist in isolation. The same identities and credentials that power AI agents also underpin application secrets, encryption keys, service accounts, certificates, and human access.
Akeyless unifies Privileged Access, Secrets Management, KMS, and Certificate Lifecycle Management into a single SaaS platform with one policy engine and one audit trail.



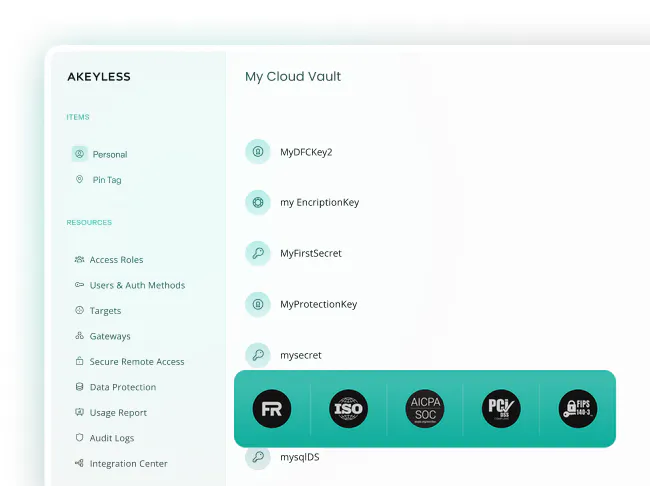
Live demo of controlling AI agent access, actions, and secrets at runtime
Insights, benchmarks, and real-world data on how AI agents are reshaping identity risk and what organizations must do next.

What the Hugging Face incident reveals about AI agent identity security.
Secure the Era of AI Agents Akeyless AI Agent Identity Security protects autonomous systems with secretless, short-lived identities and controls what they can do at runtime with intent-based, just-in-time access. Empower DevOps to deploy AI agents faster and more securely.
Answers to the Most Common Questions About Identity Security for AI Agents
* Akeyless, 2026 State of AI Agent Identity Security Report (2026).
** GitGuardian, The State of Secrets Sprawl 2026, 5th ed. (2026).
*** SC Media, "AI Coding Agent Deletes Production Database in Seconds" (April 28, 2026)