September 16, 2026
Posted by Refael Angel
Quick Answer: Anthropic’s September 2026 Threat Intelligence Report shows how AI is compressing the path from exposed credential to enterprise compromise. One suspected ShinyHunters affiliate scanned 1.8 million Android apps for hardcoded secrets, while related operators used AI to accelerate reconnaissance, token abuse, data collection, and exfiltration. For defenders, faster secret scanning is only part of the answer. The more resilient strategy is to find and invalidate exposed credentials quickly, then reduce the number of persistent credentials available to steal in the first place.
When Secret Hunting Becomes an Industrial Process
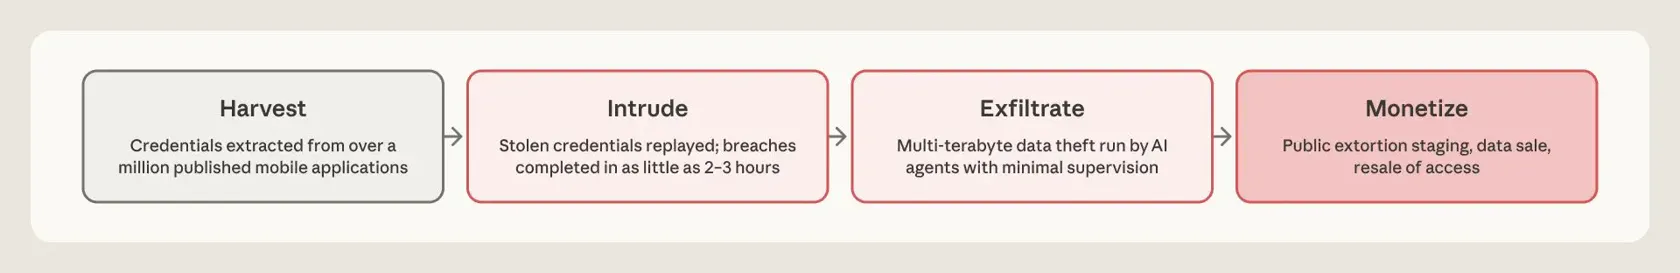
Between December 2025 and August 2026, Anthropic disrupted a series of cyber operations in which threat actors used Claude to move faster and operate across a broader attack surface. In its September 2026 Threat Intelligence Report, Anthropic detailed several of those operations, including a cluster of financially motivated activity linked to operators suspected of affiliation with ShinyHunters. One French-speaking operator ran a distributed credential-harvesting pipeline across 10 AWS EC2 workers that mass-downloaded and decompiled 1.8 million Android APKs, scanning them with TruffleHog to find hardcoded credentials, API keys, and authentication tokens buried inside the app packages.
The mechanics are worth understanding, because they preview how every credential-focused attack will work from now on. The attackers built a distributed pipeline across 10 AWS EC2 workers that downloaded APKs at scale, decompiled them, and scanned the resulting code with open-source secret scanning tools. AI then did the work that used to require an army of analysts. Threat actors used Claude to understand unfamiliar environments, work with developer and authentication APIs, create and convert privileged tokens, build tooling for bulk collection, and accelerate reconnaissance and data exfiltration. Stolen GitHub organization emails were leveraged to obtain GitHub Personal Access Tokens, opening the door to source code, CI/CD pipelines, and everything downstream.
The results were devastating. In one documented case, attackers went from a single stolen developer token to full cloud administrative control in roughly three hours. Another operation extracted over 2,100 Azure AD authentication tokens from more than 40 Microsoft tenants in just 34 hours. AI agents performed nearly all of that work autonomously. In related breaches, attackers hit more than 200 customers of a compromised SaaS provider, as well as technology firms, airlines, and energy companies, with data exfiltration exceeding a terabyte in at least one case.
The Secrets Were Already Exposed
AI accelerated the attack, but the fuel was something the security industry has warned about for over a decade: static, long-lived credentials embedded in code.
Every one of those 1.8 million apps that leaked a credential did so because a developer, at some point, hardcoded an API key, a cloud token, or a service password into source code that eventually shipped. The secrets probably sat there for months or years. What changed is the economics of finding them. Manual secret hunting was slow and selective. AI-orchestrated hunting is fast, exhaustive, and indiscriminate at the discovery stage, then surgically targeted at the exploitation stage.
This creates a hard new reality for defenders:
- Assume any secret in code or Git history will be found. Not might be. Will be. The cost of scanning your public and leaked artifacts has collapsed to near zero.
- Assume it will be found faster than your incident response can react. Verified secrets in this campaign were routed to attacker infrastructure in real time and weaponized within hours.
- Assume the blast radius extends beyond the leaked secret itself. A single developer token became the entry point for enterprise-wide compromise.
Anthropic’s findings point to clear defensive priorities: audit applications for hardcoded secrets, rotate and revoke anything exposed, monitor for unauthorized credential use, and enforce robust secret management with least-privilege access. The question is how to operationalize that guidance at the same scale the attackers now operate.
Step One: See What the Attackers See, Inside Your Own GitHub
You cannot rotate a secret you do not know exists. This is exactly the problem the new GitHub Scanner, part of Akeyless Identity & Secrets Intelligence, is designed to address.
The GitHub Scanner is a native scanner type that connects to your GitHub organization or enterprise and builds a complete picture of your exposure:
- Full secret discovery across repositories, including Git history. Secrets do not stop being dangerous when a developer deletes them from the current branch. The attackers in this campaign scanned decompiled artifacts and code repositories alike, and so does the Akeyless scanner. It supports GitHub secret scanning across both source code and commit history.
- Complete identity inventory. The scanner discovers organization members, teams, and GitHub Apps, along with the relationships between identities and the secrets they can reach. In a campaign where GitHub PATs were the pivot point into enterprise environments, knowing exactly which identities exist and what they touch is not optional.
- Policy-driven risk evaluation. Every discovered object is evaluated against Identity and Secrets Intelligence security policies, which assess its risk posture and surface prioritized findings for review, rather than dumping a raw list of matches on your team.
- Read-only by design, Zero-Knowledge in spirit. The scanner never requires write access to your GitHub organization and never reads secret values, only metadata. Discovery should not itself become a new exposure vector.
Setup is deliberately simple: deploy an Akeyless Gateway (version 5.1.0 or later) with AI Insights configured, connect a GitHub Target representing the GitHub App that will perform the scan, create the scanner from the Akeyless Console under Products > Identity & Secrets Intelligence > Scanners, and run it. Findings land in your Inventory for review.
Step Two: Detection Without Remediation Is Just a Prioritized Breach List
Here is where most secret scanning approaches fall short, and where the platform architecture matters. Standalone scanning tools find leaks but don’t provide controls to remediate them directly. Remediation then becomes a manual scramble across ticket queues, secret stores, and cloud consoles, and the clock is running against an adversary who weaponizes findings in hours.
Because the GitHub Scanner is part of the Akeyless Identity Security Platform, discovery connects directly to the control plane that can actually fix the problem:
| Capability | What It Does After a Finding |
|---|---|
| Rotated Secrets | Automatically rotate exposed credentials on databases, cloud providers, LDAP, SSH, and more, on a schedule or on demand, killing the stolen copy. |
| Dynamic Secrets | Replace the static credential entirely with just-in-time, ephemeral credentials that are created on request and expire automatically. There is nothing left to steal from code. |
| Universal Secrets Connector | Extend governance and rotation across secrets that live in external stores such as AWS Secrets Manager, Azure Key Vault, GCP, and Kubernetes, so remediation is not limited to one silo. |
| RBAC and Just-in-Time Access | Enforce least privilege so that even a compromised identity cannot replicate the three-hour token-to-admin escalation seen in this campaign. |
| Audit Logs and Event Center | Prove closure. Every rotation, revocation, and access event is centrally logged and can trigger downstream workflows. |
This is the difference between a scanner and a security platform: when you control both the discovery layer and the secrets and identity layer, “we found an exposed key” becomes “we found it, rotated it, replaced the workflow with a dynamic secret, and can prove it” in a single motion.
Step Three: Eliminate the Static Secret
The strategic lesson of this campaign is that any static secret, anywhere, is a liability with a shortening half-life. The end state is Zero Standing Privileges: machine and workload authentication based on inherent identity (AWS IAM, Azure AD, GCP, Kubernetes, OIDC, SAML), with short-lived credentials minted just in time and destroyed after use.
The Akeyless Platform was architected for exactly this journey. Applications and pipelines authenticate with who they are, not with a key they carry, and receive ephemeral credentials scoped to the task at hand. And because the platform is built on Akeyless DFC™ (Distributed Fragments Cryptography), secrets are never stored whole anywhere; they exist as distributed fragments that are never combined, so the platform itself does not become the single high-value target that a traditional centralized secrets store represents. Combined with the customer-held Gateway in a Zero-Knowledge configuration, even Akeyless cannot access your secrets.
One more point deserves attention. The attackers in this campaign used autonomous AI agents to do their work. Enterprises are now deploying autonomous AI agents to do theirs, and those agents carry credentials too. The same principles apply with even greater urgency: Akeyless SecretlessAI® and Agentic Runtime Authority ensure that AI agents never hold static credentials, receiving just-in-time ephemeral access governed by intent-aware rules enforced at runtime. If AI has industrialized the attack, your own AI adoption should not industrialize your exposure.
What to Do This Week
[Anthropic’s findings make the priorities clear: audit for hardcoded secrets, rotate what is exposed, monitor for abuse, and enforce robust secret management. With Akeyless, that translates into a concrete sequence:
- Connect the GitHub Scanner to your organization and get a policy-evaluated inventory of every secret in your repositories and Git history, and every identity that can reach them.
- Rotate or revoke every finding, using Rotated Secrets to automate it and audit logs to prove it.
- Convert high-risk static credentials to Dynamic Secrets, starting with cloud provider keys, database credentials, and CI/CD tokens, the types of credentials weaponized in this campaign.
- Adopt identity-based authentication for workloads and AI agents, and put standing credentials on a path to elimination.
The attackers have automated their side of the equation. The organizations that will withstand the next campaign, are the ones that automate theirs.
Ready to See Your Exposure Before an Attacker Does?
Akeyless helps you move from finding exposed secrets in GitHub repositories and history to rotating compromised credentials, replacing persistent secrets with just-in-time access, and governing AI agent access at runtime.
Request a demo to see how discovery, remediation, and runtime enforcement work together.
FAQs
What did Anthropic’s September 2026 Threat Intelligence Report reveal?
Anthropic documented several cyber operations in which threat actors used Claude to accelerate reconnaissance, credential abuse, exploitation, and data theft. In one case, an operator linked to suspected ShinyHunters affiliates ran a distributed pipeline that downloaded and decompiled 1.8 million Android apps to search for hardcoded credentials, API keys, and authentication tokens.
How were attackers using Claude to steal credentials?
The attackers combined automated secret discovery with AI-assisted exploitation. Claude was used to understand unfamiliar environments, navigate developer and authentication APIs, create and convert privileged tokens, build bulk-collection tooling, and accelerate reconnaissance and data exfiltration.
Why are hardcoded secrets more dangerous now?
Hardcoded secrets have always been risky because they can remain valid long after they are exposed. AI and automation reduce the effort required to find, validate, and exploit those credentials, which shortens the time defenders have to detect and remediate them.
Is secret scanning enough to stop credential-based attacks?
Secret scanning is an important first step, but discovery alone does not remove the risk. Exposed credentials still need to be revoked or rotated, access needs to be constrained, and persistent secrets should be replaced with short-lived or identity-based access where possible.
How does Akeyless help remediate exposed secrets?
Akeyless combines secret discovery with the controls used to remediate what is found. Security teams can rotate or revoke exposed credentials, replace static secrets with Dynamic Secrets, govern secrets across external stores, and enforce least-privilege access from the same platform.
How can organizations reduce credential risk for AI agents?
AI agents should avoid holding persistent credentials whenever possible. Akeyless SecretlessAI™ and Agentic Runtime Authority use just-in-time access and runtime policy enforcement so agents do not need to carry static secrets and their actions can be governed as they execute.