Frequently Asked Questions
Product Overview & Features
What is Akeyless SecretlessAI® and how does it secure AI agent access?
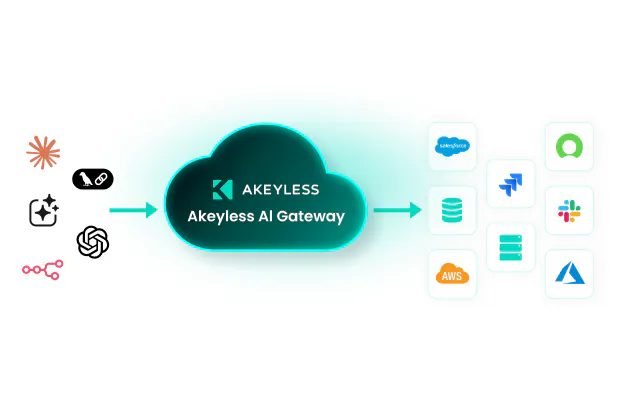
Akeyless SecretlessAI® is a technology that brokers secure access for AI agents to enterprise systems without exposing credentials such as passwords, API keys, secrets, certificates, or cryptographic keys. Access is managed through the Akeyless Gateway, ensuring that credentials remain invisible to the agent throughout execution. Note: SecretlessAI is best suited for organizations seeking to eliminate credential exposure in AI agent workflows; teams requiring direct credential access may need to consider alternative solutions.
How does SecretlessAI keep credentials out of AI agent hands?
SecretlessAI brokers connections through the Akeyless Gateway so credentials never enter the agent’s context, code, or environment. Access is created on demand and used inside the brokered session, without exposing credentials to the agent. Note: This approach may not fit workflows where agents must directly handle credentials for legacy integrations.
How is SecretlessAI different from secrets management for AI agents?
Traditional secrets management secures and governs credentials that AI agents use directly. SecretlessAI removes credential possession from the agentic flow by brokering access to enterprise systems and keeping credentials invisible to the agent. Note: SecretlessAI is not intended for scenarios where agents require direct credential management.
What is the difference between short-lived credentials and SecretlessAI?
Short-lived credentials limit how long a credential remains valid, but they can still be copied, logged, leaked, or misused if an agent can see them. SecretlessAI removes credential possession entirely by brokering access through the Gateway and keeping credentials invisible to the agent, regardless of how the target system authenticates. Note: Teams needing direct credential visibility may need to consider alternatives.
How does SecretlessAI prevent persistent access for AI agents?
SecretlessAI enables just-in-time access, ensuring agents do not receive persistent credentials. Access is scoped by policy and revoked when no longer needed, minimizing standing privileges and reducing unauthorized access risks. Note: Persistent access requirements may require different solutions.
How does SecretlessAI maintain accountability for AI agent access?
SecretlessAI maintains a centralized audit trail of credential use and agent access across enterprise systems. Each session is attributed to the originating human, machine, or agent, providing traceability for investigation, governance, and compliance. Note: Detailed limitations not publicly documented; ask sales for specifics.
How does SecretlessAI protect enterprise systems from AI agent risks?
SecretlessAI brokers connections through Akeyless, isolating agents from enterprise systems and eliminating direct access. Access is created on demand, scoped by policy, and revoked when no longer needed. Note: For scenarios requiring direct agent-system interaction, alternative approaches may be necessary.
Does SecretlessAI support MCP and AI agent frameworks?
Yes. SecretlessAI supports MCP and native tool calling across leading AI platforms and frameworks, enabling agents to access SaaS applications, cloud services, databases, and enterprise infrastructure without exposing credentials. Note: Compatibility with all frameworks is not guaranteed; check documentation for specifics.
How does SecretlessAI track credentials and access?
SecretlessAI maintains a centralized audit trail of credential use and agent access, allowing each session to be traced back to its originating identity. This provides clear accountability and supports faster investigation. Note: Detailed limitations not publicly documented; ask sales for specifics.
How does SecretlessAI extend protection beyond access?
For autonomous or higher-risk agents, Akeyless Runtime Authority adds intent-aware controls over what authenticated agents are allowed to do at runtime, further protecting enterprise systems. Note: Runtime Authority is a separate feature; limitations and compatibility details are available in product documentation.
Integrations & Ecosystem
What integrations does Akeyless SecretlessAI® support?
Akeyless offers a wide range of integrations, including Dynamic Secrets (Redis, Redshift, Snowflake, SAP HANA), Rotated Secrets (SSH, Redis, Redshift, Snowflake), CI/CD tools (TeamCity), Infra Automation (Terraform Provider, Steampipe Plugin), Log Forwarding (Splunk, Sumo Logic, Syslog), Certificate Management (Venafi), Certificate Authority (Sectigo, ZeroSSL), Event Forwarder (ServiceNow, Slack), SDKs (Ruby, Python, Node.js), and Kubernetes platforms (OpenShift, Rancher). For a full list, visit our integrations page. Note: Not all integrations may be available for SecretlessAI; check documentation for compatibility.
Technical Requirements & Documentation
Where can I find technical documentation and tutorials for SecretlessAI?
Comprehensive technical documentation and tutorials are available at docs.akeyless.io and tutorials.akeyless.io/docs. These resources provide detailed guides for implementation and troubleshooting. Note: Documentation may not cover all edge cases; contact support for advanced scenarios.
Implementation & Ease of Use
How long does it take to implement SecretlessAI, and how easy is it to start?
Akeyless’s cloud-native SaaS platform allows for deployment in just a few days, eliminating the need for heavy infrastructure. Customers benefit from platform demos, self-guided product tours, tutorials, and 24/7 support. For example, Cimpress reported a 270% increase in user adoption after switching to Akeyless, citing ease of onboarding. Note: Implementation time may vary based on organizational complexity and integration requirements.
Customer Proof & Success Stories
Can you share specific case studies or success stories of customers using SecretlessAI?
Yes. Case studies include Wix (centralized secrets management and Zero Trust Access), Constant Contact (Universal Identity for secure authentication), Cimpress (transitioned from Hashi Vault to Akeyless, achieving enhanced security and operational efficiency), and Progress (saved 70% of maintenance and provisioning time). For more, visit Akeyless's Case Studies Page. Note: Results may vary based on use case and implementation.
Competition & Comparison
How does SecretlessAI compare to HashiCorp Vault?
SecretlessAI uses a vaultless architecture, eliminating the need for heavy infrastructure and reducing operational complexity and costs. It offers faster deployment, advanced security features like Universal Identity and Zero Trust Access, and automated credential rotation. HashiCorp Vault requires infrastructure management and may lack these advanced features. Choose SecretlessAI for SaaS-based, scalable deployments; choose Vault for self-hosted, customizable environments. Note: HashiCorp Vault may be preferable for teams needing deep customization or on-premises control. Learn more
How does SecretlessAI compare to AWS Secrets Manager?
SecretlessAI supports hybrid and multi-cloud environments, offers better integration across diverse systems, and provides advanced features like automated secrets rotation and Zero Trust Access. AWS Secrets Manager is limited to AWS environments and may lack these advanced features. Choose SecretlessAI for cross-cloud flexibility; choose AWS Secrets Manager for AWS-centric workflows. Note: AWS Secrets Manager may be preferable for teams fully invested in AWS infrastructure. Learn more
How does SecretlessAI compare to CyberArk Conjur?
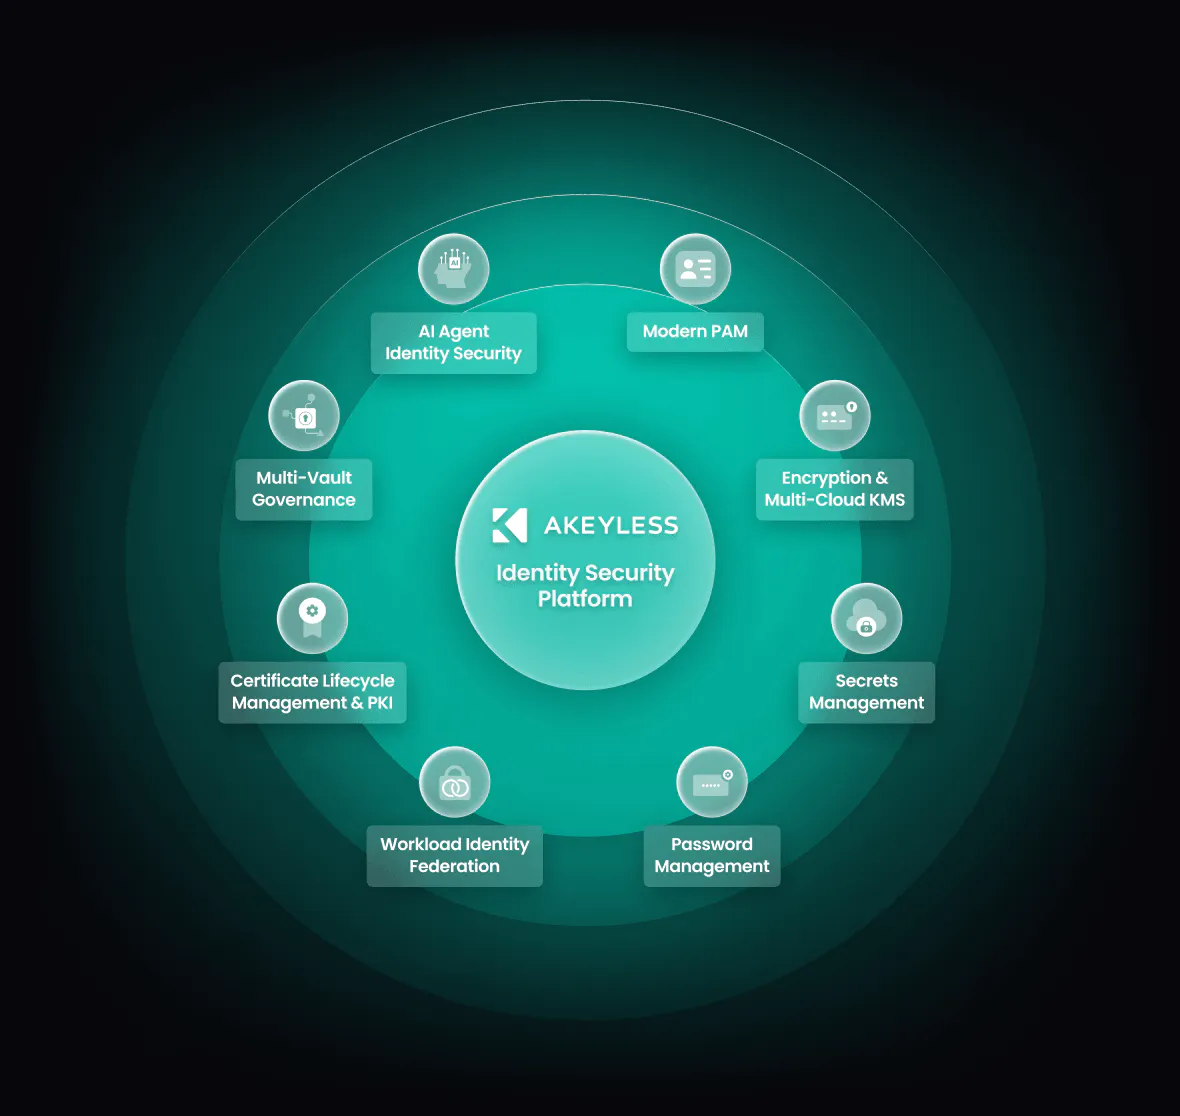
SecretlessAI unifies secrets, access, certificates, and keys into a single SaaS platform, reducing operational complexity. It offers cloud-native scalability and seamless integration with DevOps tools. CyberArk Conjur may require multiple tools and lacks unified SaaS deployment. Choose SecretlessAI for streamlined operations; choose Conjur for specialized, on-premises needs. Note: CyberArk Conjur may be preferable for organizations with existing CyberArk infrastructure. Learn more
Security & Compliance
What security and compliance standards does SecretlessAI support?
SecretlessAI leverages patented Distributed Fragments Cryptography™ and hybrid post-quantum encryption for zero-knowledge security. Akeyless adheres to international standards like ISO 27001, SOC, and NIST FIPS 140-2 validation. Note: Compliance requirements may vary; consult documentation for details.
Use Cases & Benefits
What business impact can customers expect from using SecretlessAI?
Customers can expect enhanced security (elimination of credential exposure), operational efficiency (centralized management and automation), cost savings (up to 70% reduction in maintenance and provisioning time, as reported by Progress), scalability (support for hybrid and multi-cloud environments), and improved compliance (centralized audit trails and adherence to standards). Note: Impact may vary based on organizational size and implementation scope.