


AI | Competitor | Machine IAM
The 10 Best AI Agent Identity Security Platforms for 2027Compare the best AI agent identity security platforms for securing autonomous systems, managing non-human identities, and enforcing JIT access.
AI | Competitor | Machine IAM
The 10 Best AI Agent Identity Security Platforms for 2027Compare the best AI agent identity security platforms for securing autonomous systems, managing non-human identities, and enforcing JIT access.
AI | InfoSec | Machine IAM | News
Railway Encrypted Its Customers’ Secrets but Attackers Decrypted Them AnywaySummary: Railway’s October 2026 breach exposed a critical limitation of encryption at rest: attackers who compromise the systems authorized to decrypt secrets can obtain plaintext without breaking the encryption itself. Railway confirmed that some customer environment variables were decrypted, with up to 100,000 workspaces potentially affected. The incident also disrupted deployments and triggered widespread credential […]
AI | Machine IAM
SPIFFE for AI Agents: Workload Identity and the Access ProblemSPIFFE and SPIRE give AI agents verifiable workload identities. See how Akeyless protects signing keys, brokers short-lived access, and governs actions.
AI | Machine IAM | Security
The Myth of the Solved Secret: Why Credentials Are AI’s Most Dangerous VulnerabilitySummary AI security discussions often focus on prompt injection, model vulnerabilities, and patching. But one of the most immediate risks is much more familiar: compromised credentials. AI agents require credentials to access enterprise systems and can also discover credentials exposed elsewhere. Because agents operate at machine speed and scale, even short-lived credentials can provide enough […]
AI | Security
Anthropic’s Latest Threat Report Shows How AI Is Industrializing Secret TheftQuick Answer: Anthropic’s September 2026 Threat Intelligence Report shows how AI is compressing the path from exposed credential to enterprise compromise. One suspected ShinyHunters affiliate scanned 1.8 million Android apps for hardcoded secrets, while related operators used AI to accelerate reconnaissance, token abuse, data collection, and exfiltration. For defenders, faster secret scanning is only part […]
AI | Security
EU AI Act Compliance: Mapping Identity Security ControlsThe European Union’s AI Act is the world’s first comprehensive legal framework for artificial intelligence. It takes a risk-based approach, applying stricter obligations to AI systems that could significantly affect people’s safety or fundamental rights. The regulation entered into force on August 1, 2024, with requirements phased in over time. Some provisions are already enforceable, […]
AI | Machine IAM
Zero Standing Privileges (ZSP) and Just-in-Time (JIT) Access: The New Security Standard for the AI EraZero Standing Privileges (ZSP) and Just-in-Time (JIT) access eliminate persistent credentials by granting access only when needed, for a specific task, and for a limited time.
AI | Machine IAM | Security
The Limits of Vaulting AI Agent CredentialsQuick Answer: Palo Alto Networks Unit 42 showed how a prompt-injected AWS AgentCore agent could steal and replay a credential even though it was securely stored in AgentCore Identity. The research exposes a broader problem with AI agent security: protecting credentials at rest and in transit is not enough if they become readable inside the […]
AI | Machine IAM | Security
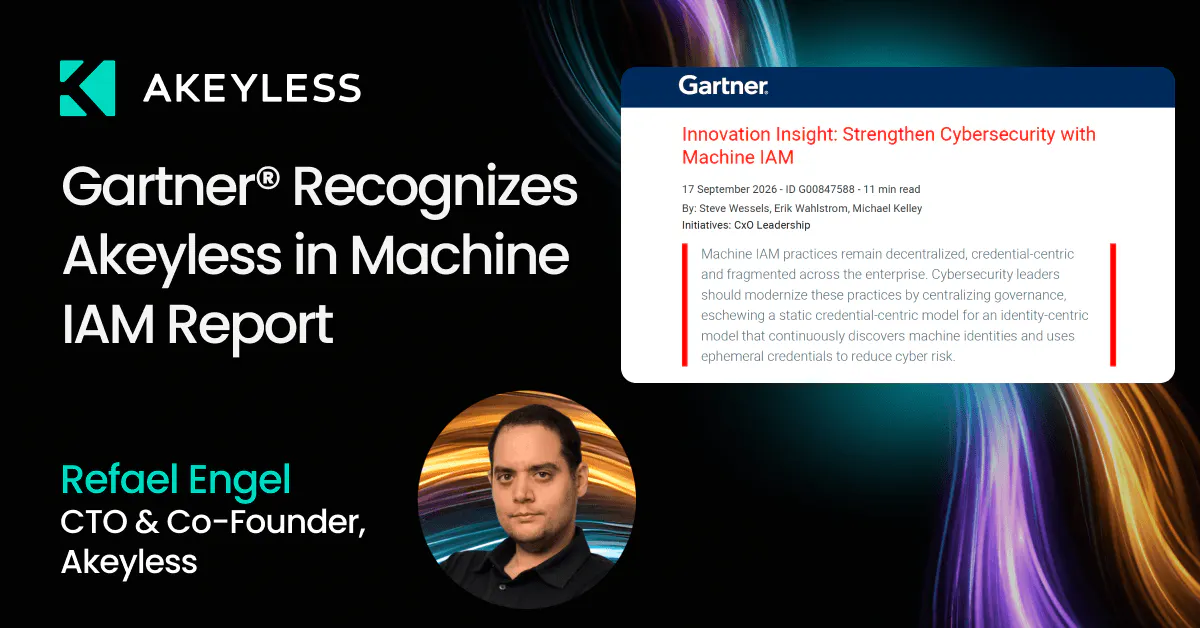
Gartner on Machine IAM: Govern the Identity, Not the CredentialQuick Answer: Machine IAM shifts security from managing credentials as standalone objects to governing the identities of workloads and AI agents directly. That means establishing who or what is requesting access, issuing short-lived authority based on policy, and maintaining ownership and lifecycle context as those identities change. For autonomous agents, that model increasingly extends into runtime, […]
AI | Platform Engineering | Security
How to Secure Credentials in AI AgentsTo secure credentials in AI agents, start by giving each agent a unique identity for the task. Limit access to only the systems and actions required, make that access short-lived, and apply intent-based access controls at runtime. Keep credentials and policy enforcement outside the agent, then revoke access as soon as the task is complete.
AI
AI Agent Runtime Identity Security For Dummies®A practical AI agent security guide for securing identities, replacing static credentials, and controlling what autonomous agents can do at runtime.

AI
AI Agent Identity Security: Why IdP-Centric IAM Falls ShortLearn why IdP-centric IAM falls short for ephemeral AI agents and how workload identity, gateway enforcement, and runtime authorization provide stronger control.