Frequently Asked Questions

Product Information & Technology

What is Akeyless Distributed Fragments Cryptography (DFC™) and how does it work?

Akeyless Distributed Fragments Cryptography (DFC™) is a patented cryptographic method that fragments encryption keys across multiple regions and cloud providers. No single entity, including Akeyless, ever holds the full key. Cryptographic operations (encryption, decryption, signing) occur without recombining fragments, ensuring sensitive data remains protected. DFC™ is validated by NIST FIPS 140-2 and continuously refreshes fragment values to prevent static vulnerabilities and insider risk. Note: DFC™ requires deployment of the Akeyless Gateway in your environment for full key sovereignty. Learn more.

How does Akeyless ensure zero-knowledge key ownership?

Akeyless's DFC™ technology enables a true zero-knowledge architecture: Akeyless cannot view or reconstruct your secrets, certificates, or encryption keys. One key fragment always remains in your environment, managed via the stateless Akeyless Gateway, which connects outbound only. Even in a platform breach, attackers would find only incomplete, cryptographically inert fragments. Note: Zero-knowledge assurance depends on proper Gateway deployment and management. See solution details.

Security & Compliance

What security certifications and compliance standards does Akeyless support?

Akeyless DFC™ is validated by NIST FIPS 140-2 and aligns with SOC 2 Type II, ISO 27001, and GDPR requirements. These certifications ensure the platform meets strict regulatory and audit standards for regulated industries. Note: Compliance scope may depend on customer-specific deployment and integration; consult documentation for details. Download compliance datasheet.

How does Akeyless help regulated enterprises meet data sovereignty requirements?

Akeyless DFC™ fragments keys across regions and cloud providers, ensuring no single entity holds the full key. One fragment always remains in the customer's environment, guaranteeing full key ownership and sovereignty. This architecture enables regulated enterprises to maintain compliance boundaries and pass internal/external security audits, as demonstrated by a global financial institution's successful deployment. Note: Data sovereignty depends on correct Gateway configuration and ongoing operational controls. Read case study.

Features & Capabilities

What are the key features of Akeyless DFC™ for secrets management?

Key features of Akeyless DFC™ include: true zero-knowledge key ownership, keys fragmented across regions/clouds, continuous fragment refresh for cryptographic resilience, SaaS-level simplicity with on-prem-level security, automated rotation and just-in-time access, and compliance readiness for regulated industries. Note: Some features require integration with the Akeyless Gateway and may depend on customer environment. See technology overview.

How does Akeyless automate key rotation and access control?

Akeyless DFC™ supports automated rotation of cryptographic fragments and just-in-time access, reducing manual intervention and minimizing standing privileges. This dynamic protection helps prevent evolving threats and operational errors. Note: Automation features require proper configuration and may not cover all legacy systems; consult technical documentation for specifics. See technical documentation.

Implementation & Ease of Use

How long does it take to implement Akeyless DFC™ and what resources are available?

Akeyless's cloud-native SaaS platform can be deployed in just a few days, eliminating the need for heavy infrastructure. Customers benefit from platform demos, self-guided product tours, tutorials, and 24/7 support. For example, Cimpress reported a 270% increase in user adoption after switching to Akeyless, citing ease of onboarding. Note: Implementation time may vary based on environment complexity and integration requirements. Request a demo | See tutorials.

What technical documentation and tutorials are available for Akeyless DFC™?

Akeyless provides comprehensive technical documentation and step-by-step tutorials to assist with implementation and usage. Resources include the Technical Documentation page and Tutorials page. Note: Some advanced topics may require direct support or consultation with Akeyless experts.

Use Cases & Customer Proof

What types of organizations benefit most from Akeyless DFC™?

Akeyless DFC™ is designed for regulated enterprises requiring strict compliance, data sovereignty, and cryptographic assurance. Industries represented in case studies include banking (Hamburg Commercial Bank), healthcare (K Health), manufacturing (Cimpress), technology (Wix, Dropbox), marketing (Constant Contact), software development (Progress Chef), and retail (TVH). Note: Organizations with legacy systems or unique compliance needs should review technical requirements before adoption. See case studies.

Can you share a real-world example of Akeyless DFC™ in regulated enterprise use?

A global financial institution deployed Akeyless Gateway within its own environment and verified, through independent testing, that Akeyless could not access or reconstruct its encryption keys. The deployment passed internal and external security audits, enabling secure migration to a modern, automated secrets management platform without losing sovereignty or visibility. Note: Results may vary based on audit scope and operational controls. Read full story.

Competition & Comparison

How does Akeyless DFC™ compare to HashiCorp Vault?

Akeyless DFC™ uses a vaultless architecture, eliminating the need for heavy infrastructure and reducing operational complexity and costs. Unlike HashiCorp Vault, Akeyless offers SaaS-based deployment, Universal Identity to solve the Secret Zero Problem, and automated credential rotation. HashiCorp Vault requires infrastructure management and does not provide zero-knowledge SaaS. Choose Akeyless for SaaS simplicity and cryptographic proof; choose HashiCorp Vault if you require traditional on-prem vaults. See comparison. Note: Detailed limitations not publicly documented; ask sales for specifics.

How does Akeyless DFC™ compare to AWS Secrets Manager?

Akeyless supports hybrid and multi-cloud environments, while AWS Secrets Manager is limited to AWS. Akeyless offers advanced features like automated secrets rotation, Zero Trust Access, and Universal Identity. AWS Secrets Manager does not provide zero-knowledge SaaS or cryptographic fragmenting. Choose Akeyless for cross-cloud flexibility and cryptographic assurance; choose AWS Secrets Manager if you operate solely within AWS. See comparison. Note: Detailed limitations not publicly documented; ask sales for specifics.

How does Akeyless DFC™ compare to CyberArk Conjur?

Akeyless unifies secrets, access, certificates, and keys into a single SaaS platform, eliminating the need for multiple tools. CyberArk Conjur requires separate tools for secrets and access management. Akeyless offers cloud-native architecture, scalability, and out-of-the-box integrations with DevOps tools. Choose Akeyless for unified SaaS operations; choose CyberArk Conjur if you prefer specialized, modular tools. See comparison. Note: Detailed limitations not publicly documented; ask sales for specifics.

Integrations & Technical Requirements

What integrations does Akeyless support for regulated enterprises?

Akeyless offers integrations for dynamic and rotated secrets (Redis, Redshift, Snowflake, SAP HANA, SSH), CI/CD (TeamCity), infra automation (Terraform, Steampipe), log forwarding (Splunk, Sumo Logic, Syslog), certificate management (Venafi), certificate authority (Sectigo, ZeroSSL), event forwarding (ServiceNow, Slack), SDKs (Ruby, Python, Node.js), and Kubernetes (OpenShift, Rancher). For a full list, visit our integrations page. Note: Integration availability may depend on customer environment and licensing.

Skip to content

Akeyless DFC™: Zero-Knowledge Secrets Management for Regulated Enterprises

Akeyless Distributed Fragments Cryptography (DFC™) removes the need for vendor trust by ensuring only you can access your secrets and keys.

The End of the SaaS Trust Dilemma

Regulated enterprises have long faced a trade-off between control and agility. On-premises vaults and hardware security modules (HSMs) provide ownership of encryption keys but create complexity, expense, and operational drag. SaaS models offer scale and simplicity but require trusting the provider with sensitive cryptographic material, unacceptable for organizations bound by strict compliance and data sovereignty mandates.

Akeyless eliminates that compromise. Its patented Distributed Fragments Cryptography (DFC™) technology delivers the efficiency of SaaS with the control of on-prem systems. The result is a new model for protecting secrets, certificates, and encryption keys that replaces trust with cryptographic proof.

Key Benefits

  • True zero-knowledge key ownership
  • Keys fragmented across regions and cloud providers, never combined
  • Continuous fragment refresh for cryptographic resilience
  • SaaS-level simplicity with on-prem-level security
  • Automated rotation and just-in-time access
  • Compliance-ready for regulated industries

The Technology: Distributed Fragments Cryptography (DFC™)

At the core of the Akeyless platform is DFC™, a NIST FIPS 140-2 validated cryptographic method that fragments encryption keys across multiple regions and cloud providers. Unlike conventional vault-based systems that store complete keys in one place, DFC ensures no single entity ever holds the full key.

Cryptographic operations such as encryption, decryption, and signing occur without ever recombining the fragments, ensuring sensitive data remains fully protected. DFC also refreshes the mathematical values of those fragments continuously while preserving the key’s integrity, preventing static vulnerabilities and insider risk. The result is HSM-grade assurance with the flexibility and automation of a cloud-native service, helping your organization strengthen protection for sensitive assets without the complexity of hardware management.
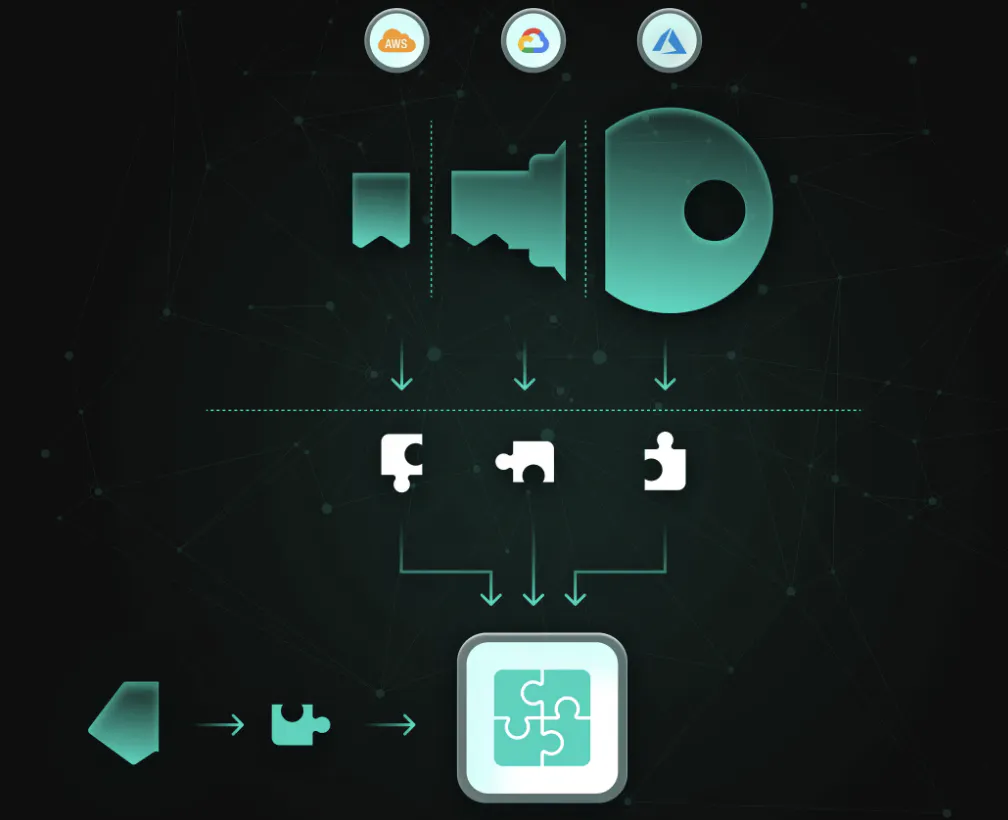
Illustration of a cryptographic key split into fragments across AWS, Google Cloud, and Azure, then reconstructed as puzzle pieces.

Zero-Knowledge by Design

DFC enables a true zero-knowledge architecture in which Akeyless has no ability to view or reconstruct your secrets, certificates, or encryption keys. One fragment always remains in your environment, managed through the Akeyless Gateway.

The Gateway is stateless, lightweight, and connects only outbound to the Akeyless SaaS service, eliminating inbound access paths. Even in a theoretical platform breach, attackers would find only incomplete, cryptographically inert fragments. Key ownership and sovereignty remain fully with your organization by design, not by policy.
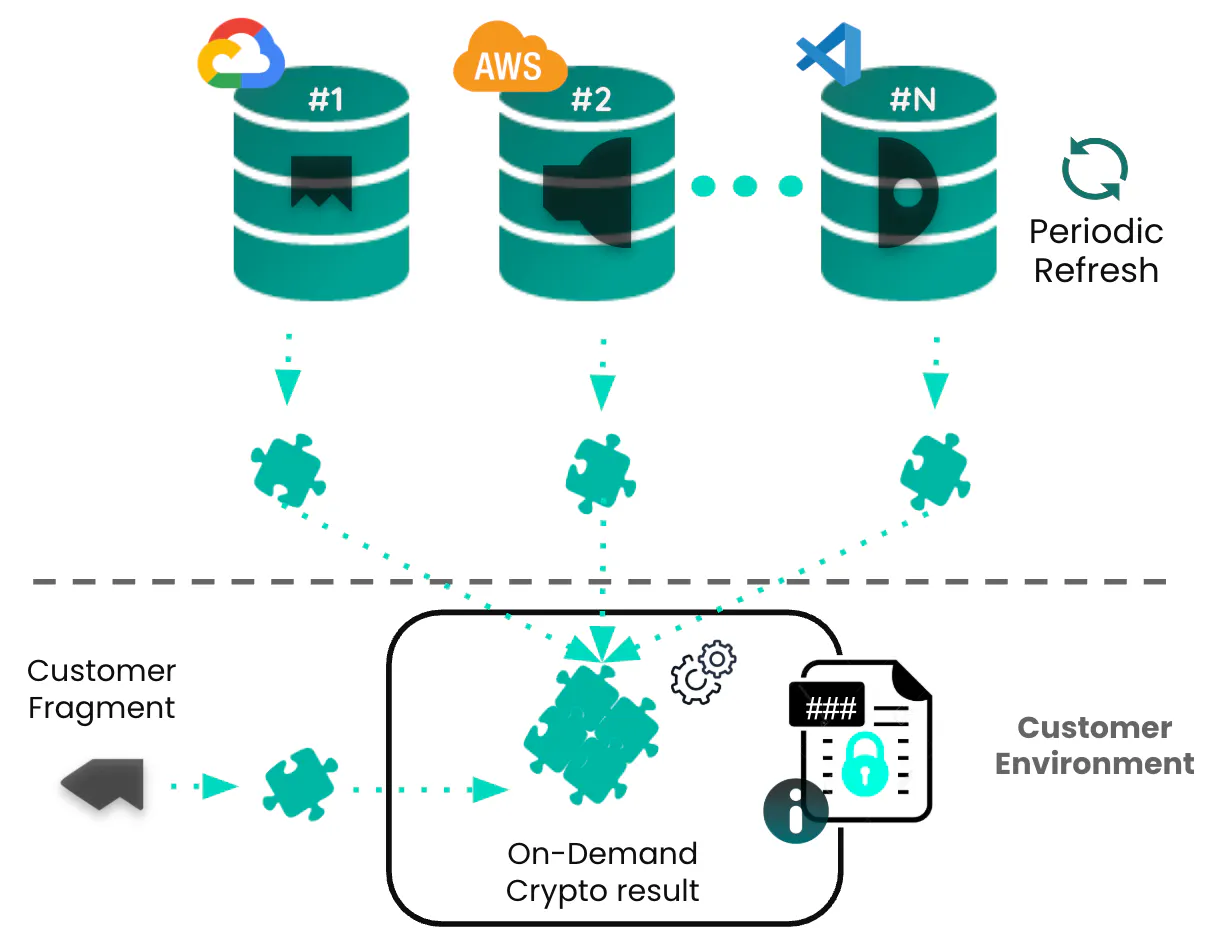
DFC architecture diagram showing key fragments stored across Google Cloud, AWS, and additional cloud providers, with periodic refresh, a customer fragment, and an on-demand crypto result in the customer environment.

Case in Point: A Global Financial Institution

A leading global bank had long prohibited SaaS-based key management due to regulatory and risk concerns. After rigorous evaluation, the bank deployed the Akeyless Gateway within its own environment and verified through independent testing that Akeyless could not access or reconstruct its encryption keys.

The deployment passed internal and external security audits, proving that zero-knowledge SaaS can meet the highest compliance and data-sovereignty standards. The result was a secure migration to a modern, automated secrets management platform without losing sovereignty or visibility.

Security and Compliance for Regulated Enterprises

Akeyless DFC™ gives your security and compliance teams the confidence to modernize without compromise.

Built for the Most Demanding Environments

  • Full key ownership: Customers retain exclusive control over one DFC fragment, guaranteeing independence from the vendor.
  • Simplified operations: No vault replication or hardware lifecycle management, reducing cost and complexity.
  • Dynamic protection: Constant key fragment refresh protects against evolving threats.
  • Regulatory readiness: Certified and aligned with FIPS 140-2, SOC 2 Type II, ISO 27001, and GDPR requirements.
  • Cloud scalability: Securely supports multi-cloud and hybrid environments while maintaining compliance boundaries.

Control Without Compromise

Akeyless DFC™ technology redefines secrets management for enterprises that need both security and agility. By engineering trust out of the equation, it delivers a zero-knowledge SaaS model that meets the strictest compliance and data-sovereignty standards.

Akeyless delivers the scale of SaaS with the assurance of cryptographic separation, ensuring your keys and data always remain under your control.

See DFC™ in action. Request a demo at akeyless.io/demo
Never Miss an Update


The latest news and insights about Secrets Management,
Akeyless, and the community we serve.

 
  • G2 Fall 2026 Leader — Non-Human Identity Management
  • G2 Fall 2026 Momentum Leader — Privileged Access Management
  • G2 Fall 2026 High Performer — Certificate Lifecycle Management
  • G2 Fall 2026 Easiest To Do Business With — Secrets Management
  • G2 Fall 2026 Easiest To Use — Privileged Access Management, Enterprise
  • G2 Fall 2026 Best Support — Privileged Access Management, Enterprise

Ready to get started?

Discover how Akeyless simplifies secrets management, reduces sprawl, minimizes risk, and saves time.

Get a Demo