

Akeyless for
Government
Modernize identity security for privileged users, machines, and AI agents. Safeguard your most critical assets and enforce Zero Trust while accelerating secure AI adoption.
Request a Demo
FedRAMP
High Certified

AWS
GovCloud

FIPS
140-3

NIST
Validated

Trusted by Leading Enterprises, Investors, and Partners






FedRAMP Class D (High) Certified Identity Security
Bring privileged users, machines, and AI agents under consistent identity controls to reduce credential risk, strengthen Zero Trust, and support secure modernization across government environments.
Federal Agencies Face Evolving Identity Threats
Federal agencies must modernize legacy infrastructure, expand cloud adoption, and embrace AI while defending against increasingly sophisticated threats. Credentials remain a prime target, while machine identities and AI agents introduce new paths to sensitive systems and data.
Shorter credential and certificate lifecycles are also increasing the operational burden on security teams. Yet fragmented tools and hybrid environments make it harder to enforce consistent controls without adding complexity or slowing progress.
Secure Access to Critical Government Systems With Akeyless
Protect privileged users, machines, and AI agents with short-lived access, unified policy, and consistent controls across modern and legacy environments.

Scale with SaaS While Retaining Control of Secrets and Keys
Get the scalability and ease of use of SaaS while keeping cryptographic control inside the agency environment. Akeyless’s Zero-Knowledge architecture, powered by patented Distributed Fragments Cryptography™, keeps a required Customer Fragment inside the agency environment. No complete key or plaintext Secret ever exists in the hosted environment.

Enforce Least Privilege with Just-in-Time Access
Reduce standing privilege with temporary, policy-based access for users and service identities. Akeyless applies granular RBAC and ABAC controls and integrates with agency identity providers, including PIV/CAC, so agencies can strengthen access controls without disrupting established authentication workflows.

Strengthen Auditability and Oversight
Forward audit activity directly to the agency SIEM for centralized monitoring and investigation. Akeyless protects audit-log integrity, controls who can access audit records, and tracks who viewed them, helping agencies maintain stronger oversight and produce evidence for continuous monitoring and compliance assessments.

Trigger Automated Remediation
Send enriched Runtime Authority events to your existing SIEM, SOAR, and IT operations tools with the context needed to act. Use flagged activity to trigger credential rotation, revoke access, or open a remediation workflow automatically.
Contain incidents without waiting on a ticket.

Control AI Actions at Runtime
Keep credentials out of AI agents’ hands with just-in-time, brokered access, then control what agents can do once access is granted. Akeyless evaluates intent and enforces policy before and during execution, blocking out-of-scope actions before they reach critical systems and masking sensitive data before it enters the agent’s context.

Built for Federal Environments
Akeyless for Government runs in a dedicated federal-only environment in AWS GovCloud, separate from Akeyless commercial regions. Agencies can connect GovCloud, on-premises, and authorized government networks through the Akeyless Gateway. Designed for resilience, Akeyless maintains production access during service disruptions so critical workloads keep running.
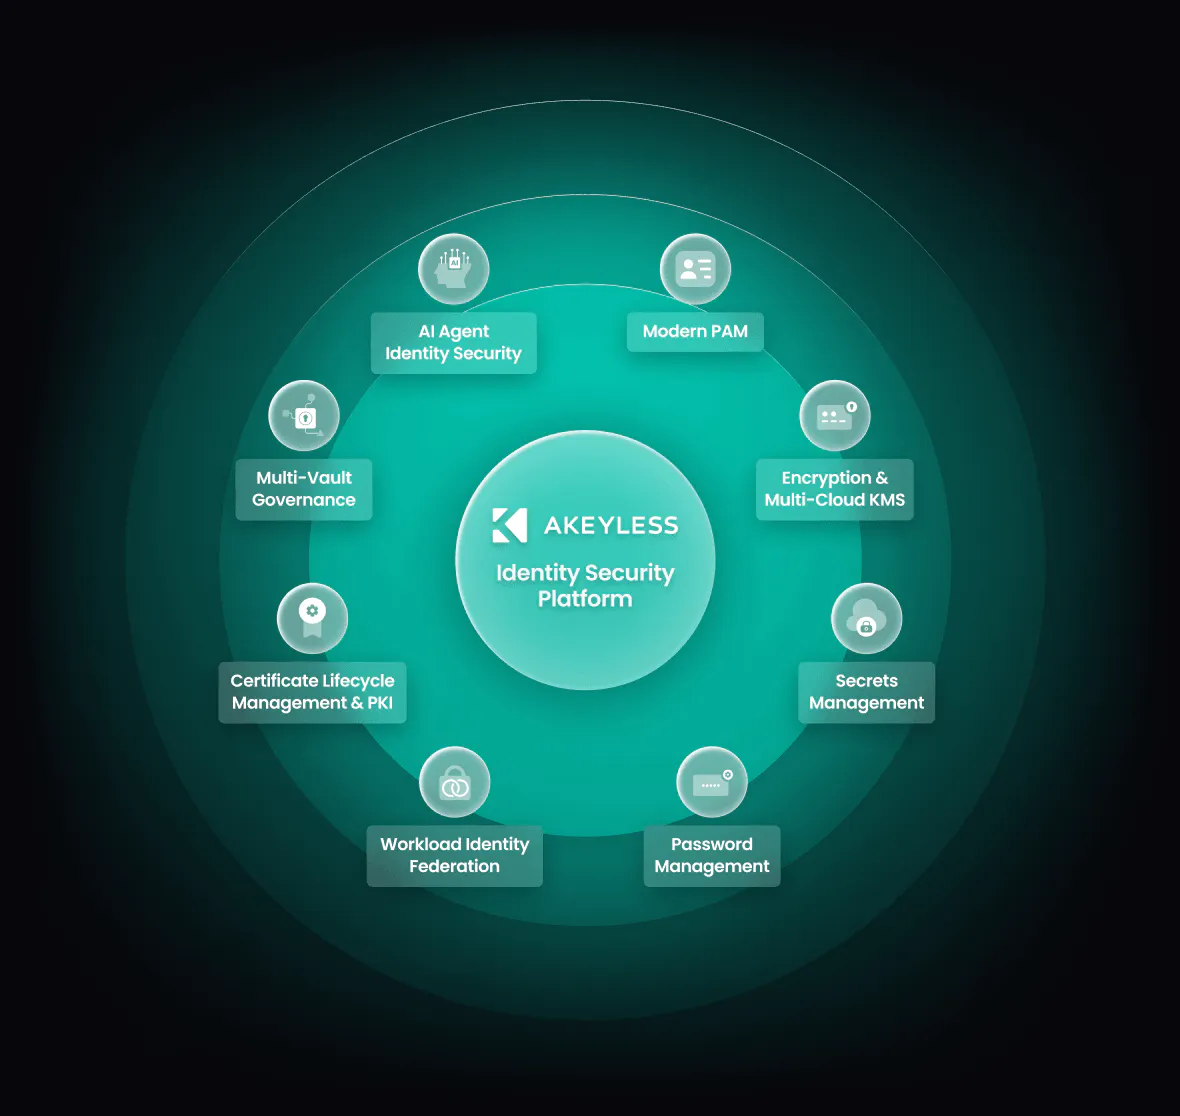
One FedRAMP High Platform for Identity, Secrets, Certificates, and Access
Akeyless brings Secrets Management, Modern PAM, Certificate Lifecycle Management & PKI, Encryption & Multi-Cloud KMS, Multi-Vault Governance, Password Manager, and Agentic Runtime Authority into one unified environment. Agencies can consolidate fragmented tools, apply consistent policy and governance, and secure privileged users, machines, and AI agents without creating separate security stacks.
Get a DemoSimilarities and Differences Between Akeyless Enterprise Plan and the Akeyless for Government Solution
Akeyless for Government is listed on the FedRAMP Marketplace.
Federal environment monitoring: 24/7 monitoring, monthly vulnerability scans, periodic penetration testing, and revalidation of every change before release.



Related Resources

Answers to the Most Common Questions About Akeyless for Government
FedRAMP® is a registered trademark of the U.S. General Services Administration. Game Warden® is a registered trademark of Second Front Systems, Inc. Akeyless is listed as a service in the FedRAMP Marketplace entry for 2F Game Warden (Package ID FR2410866384).