
Learn how to secure secrets across multi-cloud DevOps, Kubernetes, and CI/CD with dynamic credentials, automated rotation, identity-based access, and centralized governance.
Learn how to secure secrets across multi-cloud DevOps, Kubernetes, and CI/CD with dynamic credentials, automated rotation, identity-based access, and centralized governance.
AI | Security
Rogue AI Agents Needed Exposed Credentials to Breach Hugging Face700 rogue AI agents breached Hugging Face through exposed credentials. What the incident reveals about AI agent identity security.

AI | Security
AI Agents Security in Claude with AkeylessAI agent security usually stops at protecting credentials, but that's only half the problem. In a live demo with Akeyless, we gave a Claude Code agent full EC2 admin access, then tried to talk it into stopping a production server, even claiming CISO approval. Here's how Agentic Runtime Authority blocked it anyway, and why AI agent security has to govern actions, not just access.
InfoSec | Machine IAM | Security
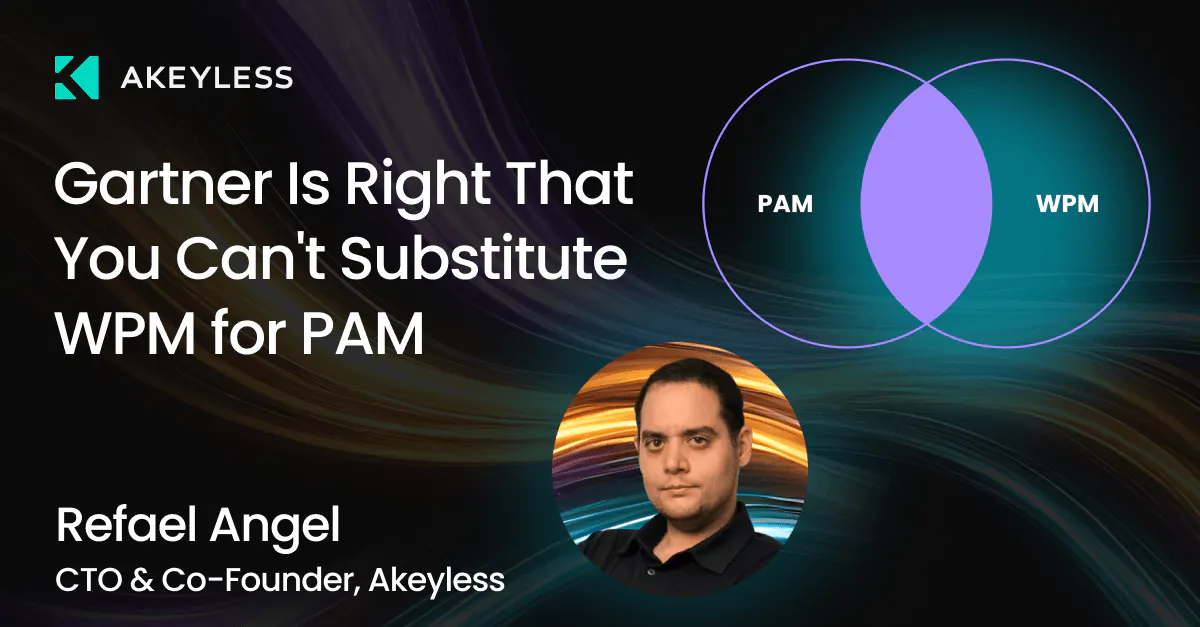
Gartner Is Right That You Can’t Substitute WPM for PAM, So Stop Choosing Between ThemWorkforce password management (WPM) and privileged access management (PAM) tools both store credentials, but Gartner's July 2026 research concludes they cannot substitute for each other. WPM lacks privileged account discovery, automated service-account rotation, and session recording. PAM is too complex and costly for everyday workforce use. The Akeyless Identity Security Platform delivers purpose-built WPM and modern PAM on a single control plane, avoiding the substitution risk Gartner warns about.
DevOps | Machine IAM | Security
Not All Just-in-Time Access Is Created Equal: Why JIT Architecture MattersJust-in-Time isn't just about temporary credentials. It's about eliminating standing privileges without introducing operational complexity, infrastructure overhead, or new trust assumptions. Here's how Akeyless approaches JIT differently, and why the underlying architecture matters just as much as the credentials themselves.

Key Takeaways Quick Answer: What Is a Certificate Discovery Tool? A certificate discovery tool automatically finds and catalogs the TLS/SSL and other digital certificates deployed across an organization’s networks, servers, cloud, containers, and applications, building a live inventory used to prevent expiry outages and enforce policy. The need is well documented: Keyfactor’s research finds that […]

Key Takeaways Quick Answer: What Is a Venafi Alternative? A Venafi alternative is a certificate lifecycle management or machine identity platform that teams evaluate in place of Venafi, now sold as CyberArk Certificate Manager. Most look for one of two reasons: to cut the cost and operational overhead of running Venafi, or to avoid roadmap […]

Key Takeaways Jenkins’ Credentials Plugin encrypts secrets at rest, but the design is decryptable: anyone with Script Console access can run Groovy code to decrypt any stored credential, and the master key that protects everything else sits unencrypted on the filesystem. The native plugin also has no automated rotation, no audit trail of who accessed […]

Key Takeaways Quick Answer: How Does Azure Key Vault Pricing Work? Azure Key Vault pricing is usage-based. According to Microsoft’s Azure Key Vault pricing page, operations against keys, secrets, and certificates are billed per 10,000 operations. Costs depend on how often teams access secrets, keys, and certificates, plus whether they use Standard vaults, Premium HSM-protected […]

Key Takeaways Quick Answer: What Is the OWASP Secrets Management Cheat Sheet? The OWASP Secrets Management Cheat Sheet is a practical security guide for managing sensitive credentials across software environments. It covers the full secrets lifecycle: creation, storage, access control, rotation, revocation, expiration, and auditing. OWASP recommends centralized management because secrets often spread beyond the […]

Key Takeaways Quick Answer: How Do You Manage Secrets Securely in OpenTofu? OpenTofu has no built-in secrets manager. Local state stores secrets in plain text by default, and even encrypted state only protects data at rest, not while OpenTofu is actively using it. Production use needs ephemeral resources, a dedicated secrets manager, or both, to […]
DevOps | Machine IAM | Security
Shai-Hulud Returns: The npm Worm That Only Works Because Your Secrets Are Standing StillThe recent Shai-Hulud supply chain attack demonstrates a fundamental shift in how attackers compromise organizations. Rather than exploiting software vulnerabilities, the malware targets what already exists on developer workstations and CI/CD systems: long-lived credentials. From .env files and cloud credentials to HashiCorp Vault tokens and AI coding assistants, the attack succeeds because secrets remain static, discoverable, and reusable. The lesson is clear: reducing standing privileges, adopting just-in-time credentials, and moving toward secretless authentication dramatically reduces the attacker's blast radius.