

See how security teams can automate certificate issuance, renewal, rotation, and compliance before shorter TLS lifecycles become the new standard.
Automate the entire certificate lifecycle from discovery to deployment while maintaining visibility, control, and compliance.
Trusted by Leading Enterprises, Investors, and Partners






Reduce operational burden, prevent outages, and stay ahead of lifecycle mandates with end-to-end automation.
Automate certificate operations, simplify PKI management, and enforce consistent standards across every certificate in your environment.
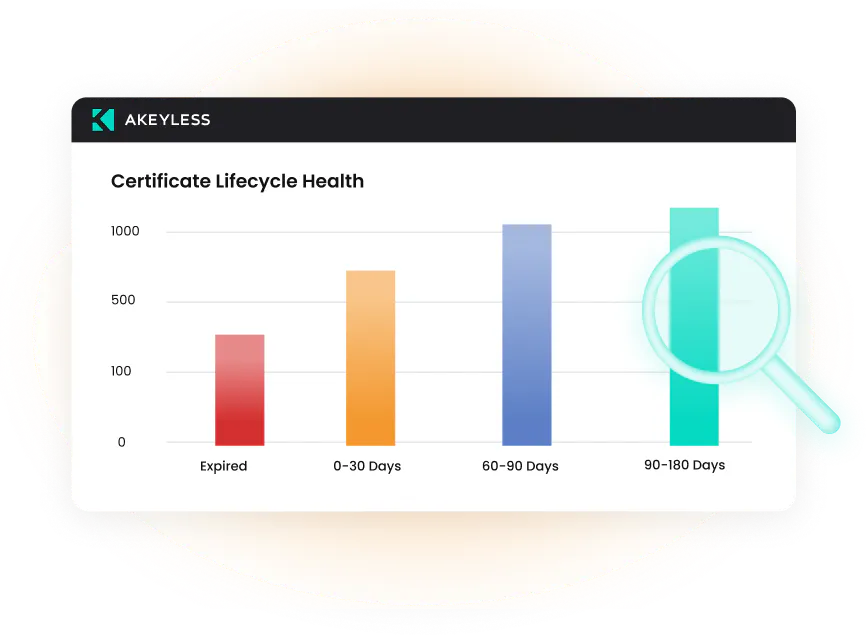
Automatically discover public and private certificates across cloud, on-prem, Kubernetes, and hybrid environments. Akeyless maintains a centralized inventory with visibility into ownership, expiration, and certificate status.
See every certificate to identify and remediate risk fast.
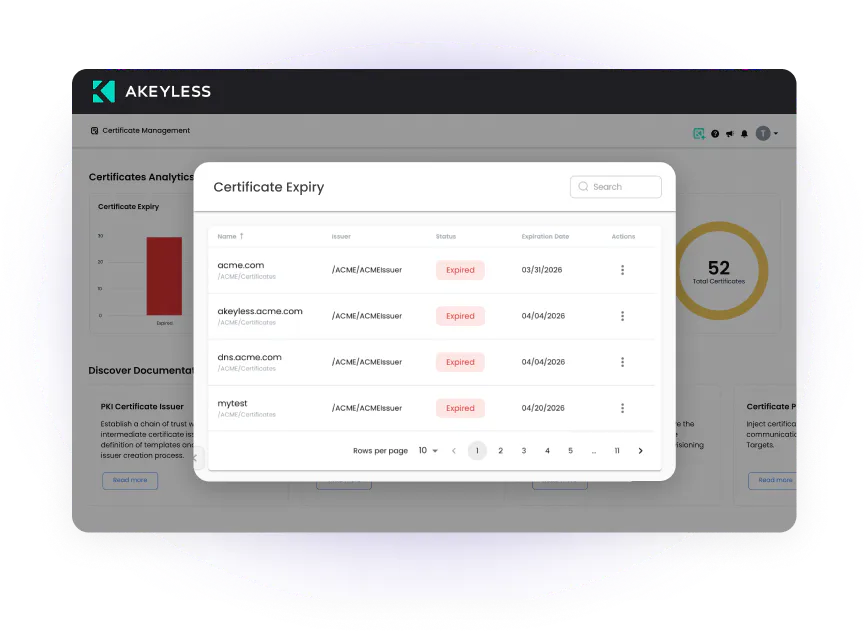
Automate certificate issuance, renewal, revocation, and deployment across your environment. Akeyless integrates with public and private CAs and supports ACME-based workflows to eliminate manual lifecycle management. Certificates can be automatically provisioned and replaced on endpoints following renewal.
Prevent outages, expired certificates, and missed renewals.
Manage certificates across public and private PKI from a single platform. Akeyless integrates with all leading certificate authorities, as well as provides built-in PKI services for securely issuing and managing certificates.
Centralize certificate operations while maintaining consistent policies across cloud, hybrid, and on-prem environments.
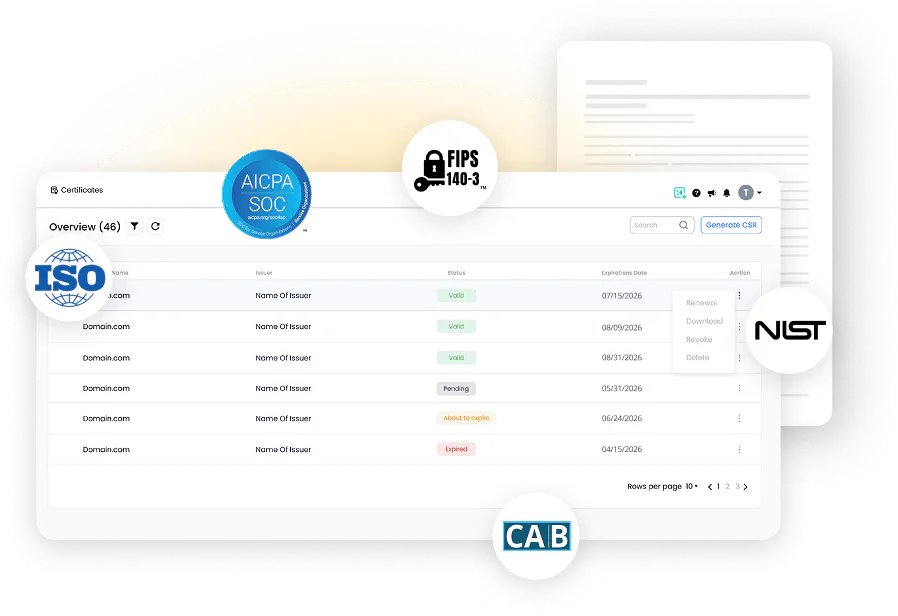
Apply consistent policies across public and private PKI through centralized governance and role-based controls. Enforce approved issuers, certificate lifetimes, and cryptographic standards while staying ahead of expirations and policy violations through automated notifications.
Ensure continuous compliance and stay crypto-agile.
Traditional certificate management relies on manual processes, disconnected tools, and fragmented PKI environments. Akeyless automates the entire certificate lifecycle through a unified platform built for modern infrastructure.
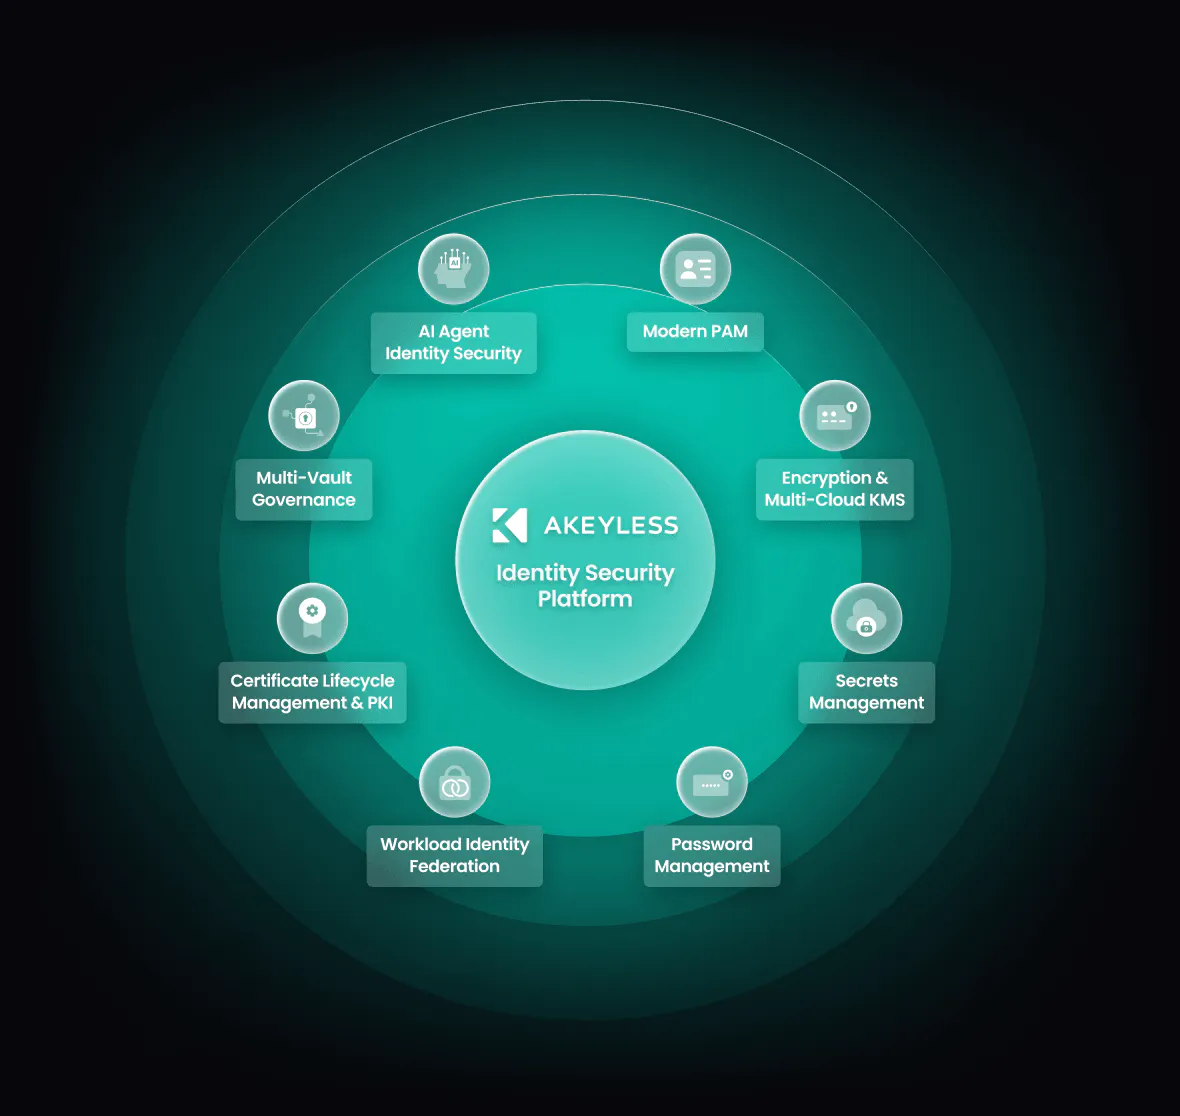
Secrets, machine identities, certificates, privileged access, and AI agents all require consistent control across modern environments. Managing them separately creates gaps in security, policy, and visibility.
Akeyless unifies Privileged Access, Secrets Management, KMS, Certificate Lifecycle Management, and AI agent security into a single SaaS platform with one policy engine and centralized governance across every identity.



Answers to the Most Common Questions About Certificate Lifecycle Management Solutions
See how security teams can automate certificate issuance, renewal, rotation, and compliance before shorter TLS lifecycles become the new standard.

Stay compliant as TLS certificates shorten to 47 days. Akeyless delivers automated lifecycle management, secure key custody, and continuous CA/B Forum–aligned renewal.

Legacy PKI systems, manual certificate tracking, and limited visibility across hybrid and multi-cloud environments are creating operational risk and compliance gaps.

Compare Akeyless vs. Keyfactor for certificate lifecycle management. Discover Keyfactor alternatives, features, pros/cons, and why Akeyless’ Zero-Knowledge unified platform is the better CLM solution.