Skip to content

Loading...

  • Competitor | DevOps | Platform Engineering

    Akeyless + Terraform: Managing Secrets in Cloud Infrastructure

    Discover how Terraform secrets management with Akeyless streamlines security for cloud infrastructure. Learn how to store, rotate, and protect secrets with zero-trust and role-based access control—without the complexity of Vault.
  • Platform Engineering | Security

    Why Secrets Sprawl Grows in Large Enterprises

    Secrets sprawl grows when enterprises add applications and access requirements without consistently updating how credentials are distributed and retired. Acquisitions introduce separate secrets stores, while deployment workflows create additional copies of credentials. As ownership and access policies diverge, security teams struggle to determine which credentials remain necessary and how to revoke them safely.

  • Platform Engineering | Security

    The Complete Guide to Multi-Vault Secrets Governance

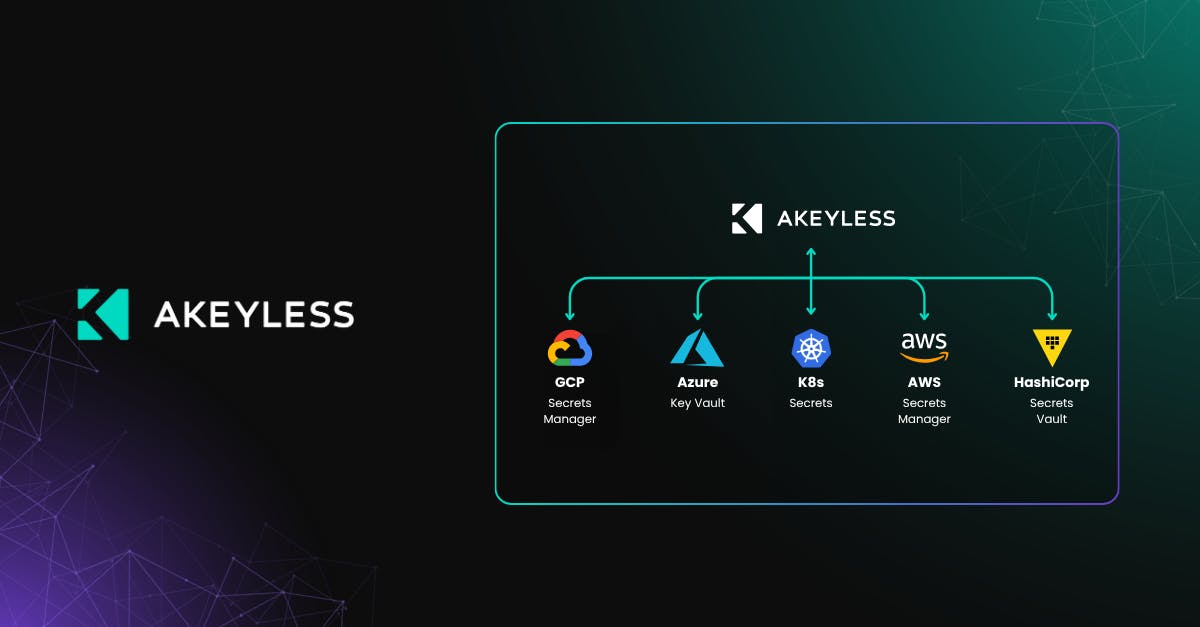
    Multi-vault secrets governance gives enterprises a consistent way to control access, rotation, and audit activity across existing secrets managers. Because those secrets can remain in AWS Secrets Manager, Azure Key Vault, Google Secret Manager, Kubernetes, or HashiCorp Vault, security teams gain clearer visibility without first moving everything into a new store.

  • AI | Platform Engineering | Security

    How to Secure Credentials in AI Agents

    To secure credentials in AI agents, start by giving each agent a unique identity for the task. Limit access to only the systems and actions required, make that access short-lived, and apply intent-based access controls at runtime. Keep credentials and policy enforcement outside the agent, then revoke access as soon as the task is complete.

  • Platform Engineering | Security

    Why Enterprise Secrets Management Fails at Scale

    Secrets management at large enterprises often breaks down when teams have to manage a growing number of credentials across systems with different access policies and rotation processes. As applications spread across cloud and on-premises environments, keeping those controls consistent takes more manual effort, and no single team has a complete view of what needs attention. Rotation gets postponed because application dependencies are unclear, while developers waiting on access find their own ways to keep deployments moving.

  • DevOps | Platform Engineering

    HashiCorp Vault Enterprise: A Cost Reality Check

    HashiCorp Vault is the default choice for secrets management for good reason. It’s powerful, flexible, and battle-tested. But when teams sit down to evaluate cost, they almost always make the same mistake: they look at the license and stop there. The license is the easy part. What’s harder to quantify, and far more significant over […]

  • InfoSec | Platform Engineering

    Secrets Migration, Minus the Drama

    Akeyless simplifies secrets migration by giving organizations two secure options: unify existing secret stores under one centralized management layer or automate migration into Akeyless when consolidation is needed. The platform connects to systems such as AWS Secrets Manager, Azure Key Vault, Google Secret Manager, HashiCorp Vault, and Kubernetes to enable full multi-vault governance without downtime or scripting.

  • DevOps | InfoSec | Platform Engineering

    Snowflake Ends Password Logins: Is Your Access Ready?

    Snowflake is phasing out password-only logins by November 2025. Learn what’s changing, who’s affected, and how Akeyless helps you secure access with key-based and passwordless authentication.

  • DevOps | Platform Engineering

    Terraform Secrets Management: Build Golden Paths for Security

    Managing secrets securely in Terraform is crucial for compliance and risk reduction. Following golden paths—best practices for secrets management—ensures consistency, security, and scalability in your Infrastructure-as-Code (IaC) workflows.

  • Platform Engineering

    Vaultless: The Future of Secrets Management

    Is your team spending too much time managing vaults instead of managing secrets? The vault-based legacy approach to manage credentials, certificates and keys has become complex, cumbersome and expensive. In this webinar Suresh Sathyamurthy, CMO of Akeyless Security, will share how the vaultless approach will help you lower costs, improve efficiency and enhance security.

  • Platform Engineering

    Akeyless ESM: Powering Unified Secrets Management for Hybrid Multi-Cloud

    In the dynamic landscape of modern enterprises, navigating the complexities of hybrid multi-cloud environments has become a common challenge. Oftentimes, organizations resort to employing separate secrets management solutions for each environment, resulting in fragmented operations and hindered governance.