Skip to content

Resources

Loading...

  • AI | Machine IAM | Security

    M2M vs. User SSO: Why SSO Stops Working When AI Starts Doing the Work

    Summary Single Sign-On (SSO) transformed how employees access enterprise applications by eliminating password fatigue and centralizing authentication. But AI assistants and autonomous agents introduce a new challenge. When an AI agent needs to connect to a system outside your SSO ecosystem, it often asks for credentials, and many users simply paste them into the conversation. […]

  • AI | Security

    AI Agents Security in Claude with Akeyless

    AI agent security usually stops at protecting credentials, but that's only half the problem. In a live demo with Akeyless, we gave a Claude Code agent full EC2 admin access, then tried to talk it into stopping a production server, even claiming CISO approval. Here's how Agentic Runtime Authority blocked it anyway, and why AI agent security has to govern actions, not just access.

  • InfoSec | Machine IAM | Security

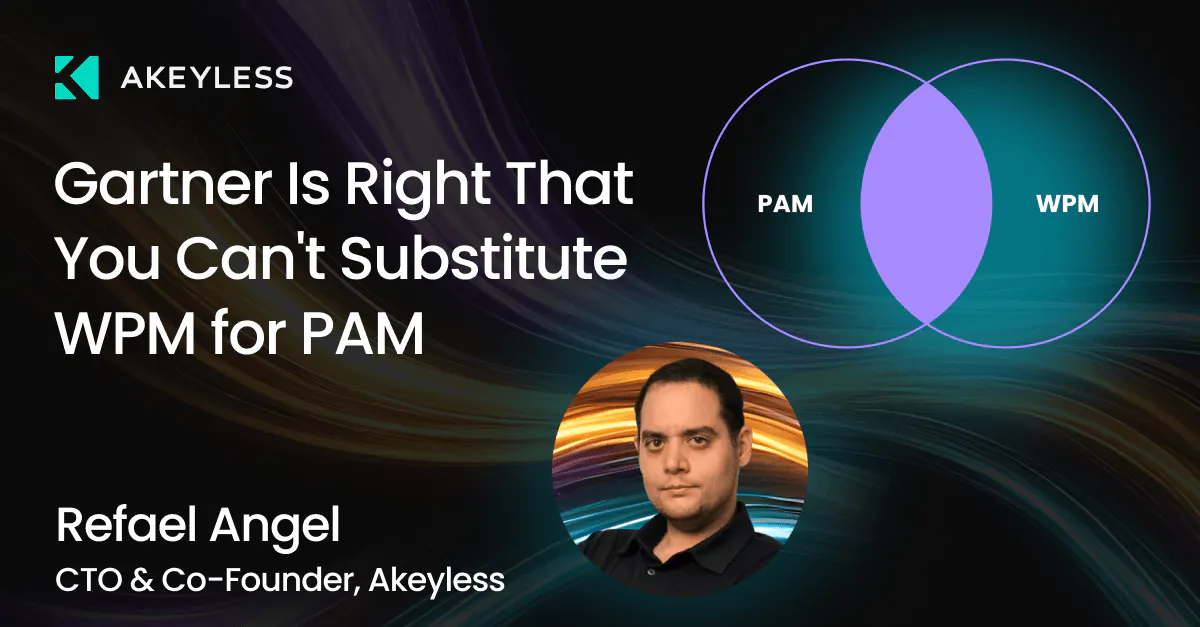
    Gartner Is Right That You Can’t Substitute WPM for PAM, So Stop Choosing Between Them

    Workforce password management (WPM) and privileged access management (PAM) tools both store credentials, but Gartner's July 2026 research concludes they cannot substitute for each other. WPM lacks privileged account discovery, automated service-account rotation, and session recording. PAM is too complex and costly for everyday workforce use. The Akeyless Identity Security Platform delivers purpose-built WPM and modern PAM on a single control plane, avoiding the substitution risk Gartner warns about.

  • DevOps | Machine IAM | Security

    Not All Just-in-Time Access Is Created Equal: Why JIT Architecture Matters

    Just-in-Time isn't just about temporary credentials. It's about eliminating standing privileges without introducing operational complexity, infrastructure overhead, or new trust assumptions. Here's how Akeyless approaches JIT differently, and why the underlying architecture matters just as much as the credentials themselves.

  • Certificate Discovery Tools: The Foundation of Certificate Management

    Key Takeaways Quick Answer: What Is a Certificate Discovery Tool? A certificate discovery tool automatically finds and catalogs the TLS/SSL and other digital certificates deployed across an organization’s networks, servers, cloud, containers, and applications, building a live inventory used to prevent expiry outages and enforce policy. The need is well documented: Keyfactor’s research finds that […]

  • Venafi Alternative: Akeyless vs Venafi Compared for 2026

    Key Takeaways Quick Answer: What Is a Venafi Alternative? A Venafi alternative is a certificate lifecycle management or machine identity platform that teams evaluate in place of Venafi, now sold as CyberArk Certificate Manager. Most look for one of two reasons: to cut the cost and operational overhead of running Venafi, or to avoid roadmap […]

  • Jenkins Secrets, Explained: What the Credentials Plugin Gets Wrong

    Key Takeaways Jenkins’ Credentials Plugin encrypts secrets at rest, but the design is decryptable: anyone with Script Console access can run Groovy code to decrypt any stored credential, and the master key that protects everything else sits unencrypted on the filesystem. The native plugin also has no automated rotation, no audit trail of who accessed […]

  • G2 Fall 2026 Leader — Non-Human Identity Management
  • G2 Fall 2026 Momentum Leader — Privileged Access Management
  • G2 Fall 2026 High Performer — Certificate Lifecycle Management
  • G2 Fall 2026 Easiest To Do Business With — Secrets Management
  • G2 Fall 2026 Easiest To Use — Privileged Access Management, Enterprise
  • G2 Fall 2026 Best Support — Privileged Access Management, Enterprise

Ready to get started?

Discover how Akeyless simplifies secrets management, reduces sprawl, minimizes risk, and saves time.

Get a Demo