Skip to content

Resources

Loading...

  • DevOps | Machine IAM | Security

    Not All Just-in-Time Access Is Created Equal: Why JIT Architecture Matters

    Just-in-Time isn't just about temporary credentials. It's about eliminating standing privileges without introducing operational complexity, infrastructure overhead, or new trust assumptions. Here's how Akeyless approaches JIT differently, and why the underlying architecture matters just as much as the credentials themselves.

  • Certificate Discovery Tools: The Foundation of Certificate Management

    Key Takeaways Quick Answer: What Is a Certificate Discovery Tool? A certificate discovery tool automatically finds and catalogs the TLS/SSL and other digital certificates deployed across an organization’s networks, servers, cloud, containers, and applications, building a live inventory used to prevent expiry outages and enforce policy. The need is well documented: Keyfactor’s research finds that […]

  • Venafi Alternative: Akeyless vs Venafi Compared for 2026

    Key Takeaways Quick Answer: What Is a Venafi Alternative? A Venafi alternative is a certificate lifecycle management or machine identity platform that teams evaluate in place of Venafi, now sold as CyberArk Certificate Manager. Most look for one of two reasons: to cut the cost and operational overhead of running Venafi, or to avoid roadmap […]

  • Jenkins Secrets, Explained: What the Credentials Plugin Gets Wrong

    Key Takeaways Jenkins’ Credentials Plugin encrypts secrets at rest, but the design is decryptable: anyone with Script Console access can run Groovy code to decrypt any stored credential, and the master key that protects everything else sits unencrypted on the filesystem. The native plugin also has no automated rotation, no audit trail of who accessed […]

  • Azure Key Vault Pricing: Cost Guide for Secrets, Keys, and Certificates

    Key Takeaways Quick Answer: How Does Azure Key Vault Pricing Work? Azure Key Vault pricing is usage-based. According to Microsoft’s Azure Key Vault pricing page, operations against keys, secrets, and certificates are billed per 10,000 operations. Costs depend on how often teams access secrets, keys, and certificates, plus whether they use Standard vaults, Premium HSM-protected […]

  • OWASP Secrets Management Cheat Sheet: Reducing Static Secrets in Practice

    Key Takeaways Quick Answer: What Is the OWASP Secrets Management Cheat Sheet? The OWASP Secrets Management Cheat Sheet is a practical security guide for managing sensitive credentials across software environments. It covers the full secrets lifecycle: creation, storage, access control, rotation, revocation, expiration, and auditing. OWASP recommends centralized management because secrets often spread beyond the […]

  • OpenTofu Secrets, Explained: Built-In vs. Production-Ready

    Key Takeaways Quick Answer: How Do You Manage Secrets Securely in OpenTofu? OpenTofu has no built-in secrets manager. Local state stores secrets in plain text by default, and even encrypted state only protects data at rest, not while OpenTofu is actively using it. Production use needs ephemeral resources, a dedicated secrets manager, or both, to […]

  • DevOps | Machine IAM | Security

    Shai-Hulud Returns: The npm Worm That Only Works Because Your Secrets Are Standing Still

    The recent Shai-Hulud supply chain attack demonstrates a fundamental shift in how attackers compromise organizations. Rather than exploiting software vulnerabilities, the malware targets what already exists on developer workstations and CI/CD systems: long-lived credentials. From .env files and cloud credentials to HashiCorp Vault tokens and AI coding assistants, the attack succeeds because secrets remain static, discoverable, and reusable. The lesson is clear: reducing standing privileges, adopting just-in-time credentials, and moving toward secretless authentication dramatically reduces the attacker's blast radius.

  • AI | Machine IAM | Security

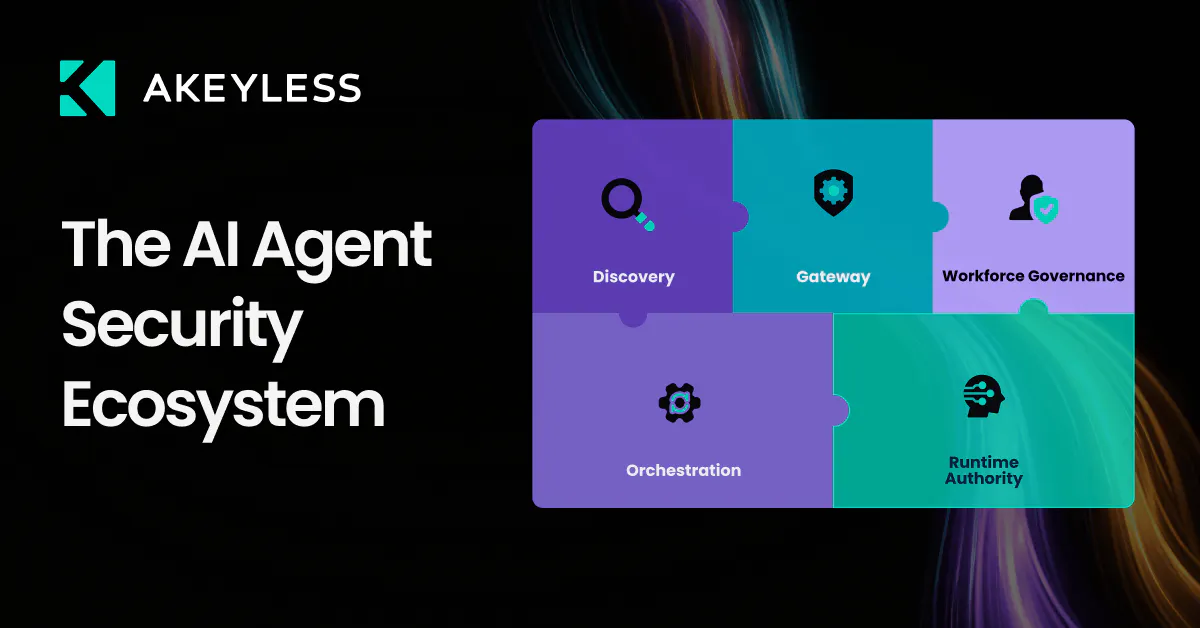
    Understanding the AI Agent Security Ecosystem: Roles, Responsibilities, and Where Runtime Authority Fits

    As enterprises deploy AI agents, an entirely new security ecosystem is emerging. AI discovery platforms, MCP gateways, workforce AI governance platforms, automation platforms, and runtime authorization solutions all promise to secure AI agents—but they solve fundamentally different problems. Understanding where each category fits is becoming just as important as choosing the right products.

  • G2 Fall 2026 Leader — Non-Human Identity Management
  • G2 Fall 2026 Momentum Leader — Privileged Access Management
  • G2 Fall 2026 High Performer — Certificate Lifecycle Management
  • G2 Fall 2026 Easiest To Do Business With — Secrets Management
  • G2 Fall 2026 Easiest To Use — Privileged Access Management, Enterprise
  • G2 Fall 2026 Best Support — Privileged Access Management, Enterprise

Ready to get started?

Discover how Akeyless simplifies secrets management, reduces sprawl, minimizes risk, and saves time.

Get a Demo